

Entrepreneur, visionary, trader,supporter and hodler of #bitcoin. Founder hege fund https://teapawt.org/t.co/RrlcyQ7dqB
Planet Earth
Joined April 2009
- Tweets26.5K
- Following4.9K
- Followers1.9K
- Likes16.7K




Pinned Tweet
⚡️ CRYPTOTRUST.ONE — ИТОГИ #SETUP · 28.09–01.11
💰 Общий PNL: +738% ✅ Profit: 9 | ❌ Loss: 7 | Винрейт: 56%
🎯 И главное:
Гипотеза «Почему Uptober не состоится» — отработана на 100%.
Кто прочитал — тот был готов:
✅ t.me/cryptotrust_one/7913
🖥cryptotrust.one/uptober/

1
1
52


ILYABOEV.COM retweeted

iphone users
hackers built an entire working computer inside a gif image and used it to take over iphones without the owner touching anything
not a virus, not a link, a fake gif sent over imessage that exploited apple's image processing to construct a full software cpu with 70,000 operations running inside the image parser
registers, memory, logic gates, a whole machine built from math before the phone even buzzed with a notification
your iphone was running someone else's computer inside a picture and you'd never know
that's pegasus, and it's still the most sophisticated attack ever found on a consumer device

When researchers analyzed how Pegasus spyware infected iPhones without the user tapping anything, they found something wild. The attackers sent an iMessage with a fake GIF that targeted Apple's image decompression engine. The decompression math was so flexible that the exploit chained arithmetic operations together to construct a literal, functioning software CPU using over 70,000 segment commands that defined logical bit operations (AND, OR, XOR, XNOR, etc.) entirely inside the image parser. This created a small computer architecture with registers, a full 64-bit adder, and a comparator, running raw code before the phone even buzzed with a notification
ILYABOEV.COM retweeted

The dot-com bubble vs the AI boom:
H/T to @lesse_jivermore for creating this awsome comparison👇
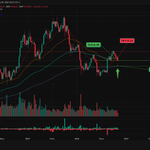
#BTC $75.6k 📉
Первый уровень поддержки моменте сломан (Дневная 200 MA) $76.5k ❗️
Следующий сильный уровень (Недельная 200 MA) $70.3k ❌↗️
Маркоэкономика + Геополитка + жирная коррекиця в AI-секторе + Возможное повышение ставки ФРС, нам как бы намекают но то что мы с большей вероятностью увидим на следующей недели BTC < $73k ( Соответствует нейросетапу t.me/cryptotrust_one/8163 от 30 октября.)

18
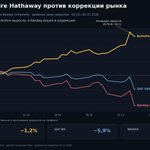
📊 Berkshire Hathaway: «Коррекция? Не слышал»
Пока рынок распродаёт AI-акции, холдинг Баффета держится заметно спокойнее.
Данные на закрытие 05.11.2026:
🔸 BRK.B: +13,9% с 2 октября; всего −1,2% от рекордного закрытия $579,09.
🔸 S&P 500: −4,8% с 2 октября; −5,9% от октябрьского максимума.
🔸 Nasdaq: −10,6% с 2 октября; −11,9% от максимума. Это уже коррекция.
📉 Только за 5 ноября: Berkshire −1,2%, S&P 500 −4,4%, Nasdaq −5,5%.
⚠️ Но Berkshire — не «неубиваемый» актив, а отдельная акция. Она тоже может падать.
📌 Сработала не только диверсификация бизнесов холдинга, но и ротация из дорогих AI/growth в value и защитные компании.
Диверсификация не отменяет падения. Она снижает зависимость портфеля от одного рыночного сценария.t.me/cryptotrust_one/8250

18

ILYABOEV.COM retweeted

🚨 IF YOU ARE IN CRYPTO, IGNORE THIS POST AT YOUR OWN RISK
A friend lost $535,000 USDT yesterday, and he even sent a test transfer first. His wallet wasn't hacked and his keys never leaked. He lost it to a bot.
The test transfer arrived fine. Within seconds, a bot sent 1 USDT to his wallet from a fake address that started and ended with the same characters as the real one. Now the fake address was sitting in his transaction history, right next to the real one.
When he went to send the full amount, he copied the address from that history and picked the fake one. The money was gone in under 30 seconds, swapped out of USDT before Tether could freeze it.
This is called address poisoning, and it's running at industrial scale. The bot that got him has run over 6 million transactions, and it goes after anyone moving large amounts.
Here's how to make sure it never happens to you:
• Never copy an address from your transaction history or a block explorer
• After a test transfer, copy the address again from the original message the receiver sent you
• Check every character, because these bots match both the start and the end
• Save verified addresses in your wallet's address book with names
Now open your wallet and go through your history. If there's a tiny deposit from an address you don't recognize, a bot has already marked you. Tell me below if you find one.
Repost this post and share this to the person you know who moves the most money on-chain.


✅ $2 трлн уничтожено на фондовом рынке США за 50 минут. То, что началось как коррекция в полупроводниках, переросло в массовую распродажу по всему рынку – Dow Jones -2%, Nasdaq -5% и S&P 500 -3%. Лидеры по потерям: Nvidia -8%, SpaceX -10% и Tesla -10% ☠️
42
#BTC $76K🔽
1.🕯 Уровень $76.5k -критический уровень, 27 октября..
2.🐻Сработал медвежий сценарий о котором писал днем:
потеря 77 900 → возврат к 76 200–75 670
Ниже $75 670 структура отскока ломается.t.me/cryptotrust_one/8237

14
ILYABOEV.COM retweeted
JUST IN: 🇷🇺 Russia's largest stock exchange, the Moscow Exchange, will start trading Bitcoin on December 1 🚀
ILYABOEV.COM retweeted

‼️ Opening a website was enough to hand unpatched iOS and Android phones to Russian hackers, Sekoia says.
They poisoned a Ukrainian analytics tool used by hundreds of sites to steal messages, passwords and cookies.
They only used known vulnerabilities that were already patched.


На рынках американские горки 🎢
#BTC $77.7k 📉
🫡 Сoinglass: За 1 час ликвидировано LONG-позиций на $401,000,000+
Страхи, что демократы замедлят развитие ИИ и строительство дата-центров, обвалили производителей полупроводников и ПО 🔽
Nvidia (-5%) официально перешла на медвежий рынок – 22% ниже пика.
Досталось и Илону Маску, основной бизнес которого сосредоточен в Техасе, а республиканцы проиграли его впервые с 1988 года:
▶️ Tesla -9%
▶️ SpaceX -7,5% t.me/cryptotrust_one


45

ILYABOEV.COM retweeted

🚨🇷🇺 Russian Police Arrest Three Suspected VasyGrek Hackers and Dismantle Cybercrime Infrastructure
Russian authorities have arrested three suspected members of VasyGrek, also known as Fluffy Wolf, a financially motivated cybercrime group linked to attacks against Russian and international organizations since 2016.
Police searched the suspects' homes and offices, seizing computers, communication devices, and other evidence. The group allegedly used phishing emails disguised as financial documents to distribute malware, steal credentials, and gain unauthorized access to corporate systems.
In one September 2025 attack, the group allegedly stole approximately $8,000 from a company's bank account after an employee opened a malicious document.
Kaspersky also identified more than 100 attempted attacks between January and September 2026, primarily targeting organizations in Russia, Belarus, and Kazakhstan.
VasyGrek | Attack Details
• Active since: 2016
• Suspects arrested: 3
• Attacks observed in 2026: 100+
• Initial access: Phishing emails and malicious attachments
• Malware: MetaStealer, PureCrypter, WarZone RAT, PureRAT, and others
• Targeted sectors: Government, energy, finance, healthcare, manufacturing, and agriculture
The group relied on phishing infrastructure, foreign-hosted servers, and remote access tools to compromise victims and steal funds.
Authorities say the operation disrupted the group's criminal infrastructure, although the full extent of its activities remains under investigation.

ILYABOEV.COM retweeted

If you design with AI, this is all you need
1. studio.motionsites.ai — cheaper than lovable
2. motionsites.ai — premium website prompts: 800+ 3d websites, motion sections. Paste into Claude, ship.
3. land-book.com — landing page inspiration done right.
4. recent.design— cool gallery for web design inspo
5. landdding.com — top notch landings
6. fontinlogo.com — fonts behind brands
7. godly.website — award websites
8. 60fps.design — mobile UI animations
save these for your next project