

Entrepreneur, visionary, trader,supporter and hodler of #bitcoin. Founder hege fund https://teapawt.org/t.co/RrlcyQ7dqB
Planet Earth
Joined April 2009
- Tweets26.5K
- Following4.9K
- Followers1.9K
- Likes16.7K




ILYABOEV.COM retweeted

iphone users
hackers built an entire working computer inside a gif image and used it to take over iphones without the owner touching anything
not a virus, not a link, a fake gif sent over imessage that exploited apple's image processing to construct a full software cpu with 70,000 operations running inside the image parser
registers, memory, logic gates, a whole machine built from math before the phone even buzzed with a notification
your iphone was running someone else's computer inside a picture and you'd never know
that's pegasus, and it's still the most sophisticated attack ever found on a consumer device

When researchers analyzed how Pegasus spyware infected iPhones without the user tapping anything, they found something wild. The attackers sent an iMessage with a fake GIF that targeted Apple's image decompression engine. The decompression math was so flexible that the exploit chained arithmetic operations together to construct a literal, functioning software CPU using over 70,000 segment commands that defined logical bit operations (AND, OR, XOR, XNOR, etc.) entirely inside the image parser. This created a small computer architecture with registers, a full 64-bit adder, and a comparator, running raw code before the phone even buzzed with a notification
ILYABOEV.COM retweeted

The dot-com bubble vs the AI boom:
H/T to @lesse_jivermore for creating this awsome comparison👇
ILYABOEV.COM retweeted

🚨 IF YOU ARE IN CRYPTO, IGNORE THIS POST AT YOUR OWN RISK
A friend lost $535,000 USDT yesterday, and he even sent a test transfer first. His wallet wasn't hacked and his keys never leaked. He lost it to a bot.
The test transfer arrived fine. Within seconds, a bot sent 1 USDT to his wallet from a fake address that started and ended with the same characters as the real one. Now the fake address was sitting in his transaction history, right next to the real one.
When he went to send the full amount, he copied the address from that history and picked the fake one. The money was gone in under 30 seconds, swapped out of USDT before Tether could freeze it.
This is called address poisoning, and it's running at industrial scale. The bot that got him has run over 6 million transactions, and it goes after anyone moving large amounts.
Here's how to make sure it never happens to you:
• Never copy an address from your transaction history or a block explorer
• After a test transfer, copy the address again from the original message the receiver sent you
• Check every character, because these bots match both the start and the end
• Save verified addresses in your wallet's address book with names
Now open your wallet and go through your history. If there's a tiny deposit from an address you don't recognize, a bot has already marked you. Tell me below if you find one.
Repost this post and share this to the person you know who moves the most money on-chain.


ILYABOEV.COM retweeted
JUST IN: 🇷🇺 Russia's largest stock exchange, the Moscow Exchange, will start trading Bitcoin on December 1 🚀
ILYABOEV.COM retweeted

‼️ Opening a website was enough to hand unpatched iOS and Android phones to Russian hackers, Sekoia says.
They poisoned a Ukrainian analytics tool used by hundreds of sites to steal messages, passwords and cookies.
They only used known vulnerabilities that were already patched.


ILYABOEV.COM retweeted

🚨🇷🇺 Russian Police Arrest Three Suspected VasyGrek Hackers and Dismantle Cybercrime Infrastructure
Russian authorities have arrested three suspected members of VasyGrek, also known as Fluffy Wolf, a financially motivated cybercrime group linked to attacks against Russian and international organizations since 2016.
Police searched the suspects' homes and offices, seizing computers, communication devices, and other evidence. The group allegedly used phishing emails disguised as financial documents to distribute malware, steal credentials, and gain unauthorized access to corporate systems.
In one September 2025 attack, the group allegedly stole approximately $8,000 from a company's bank account after an employee opened a malicious document.
Kaspersky also identified more than 100 attempted attacks between January and September 2026, primarily targeting organizations in Russia, Belarus, and Kazakhstan.
VasyGrek | Attack Details
• Active since: 2016
• Suspects arrested: 3
• Attacks observed in 2026: 100+
• Initial access: Phishing emails and malicious attachments
• Malware: MetaStealer, PureCrypter, WarZone RAT, PureRAT, and others
• Targeted sectors: Government, energy, finance, healthcare, manufacturing, and agriculture
The group relied on phishing infrastructure, foreign-hosted servers, and remote access tools to compromise victims and steal funds.
Authorities say the operation disrupted the group's criminal infrastructure, although the full extent of its activities remains under investigation.
ILYABOEV.COM retweeted

If you design with AI, this is all you need
1. studio.motionsites.ai — cheaper than lovable
2. motionsites.ai — premium website prompts: 800+ 3d websites, motion sections. Paste into Claude, ship.
3. land-book.com — landing page inspiration done right.
4. recent.design— cool gallery for web design inspo
5. landdding.com — top notch landings
6. fontinlogo.com — fonts behind brands
7. godly.website — award websites
8. 60fps.design — mobile UI animations
save these for your next project

ILYABOEV.COM retweeted

🚨this is going to END some careers.
a dev just dropped a free Claude skill called "teardown" and anyone who animates 3d for money should pay attention.
the skill is ridiculously good but the dev is crazy enough to give it away anyway.
how it runs:
> you hand it a picture and say what the creature is
> claude codes the octopus, renders a still beside your picture and patches the differences round after round before any animation
> every arm is a chain of links that shrink toward the tip, so each one curls into a true spiral with 2 rows of suction wheels underneath
> one timeline drives the whole thing: the jet gauge, the operator's cursor, the console rows and the audio all tick off it
> it can't watch footage, so it reviews a grid of frames at every beat, fixes what looks off and re-renders until a full pass comes back clean
> the frames come off your own GPU at 60 fps and python writes the soundtrack on the same beats
one picture went in and this octopus is what came back out.
free skill, full write-up in the article 👇


ILYABOEV.COM retweeted
‼️ BREAKING: Hackers say they stole 23TB from Russia's statistics agency Rosstat, including data on Russian military losses in Ukraine.
Belarus's Cyber Partisans and Silent Crow claim they took over ~25,000 machines and destroyed internal systems at its headquarters and regional offices.
Rosstat confirms targeted destructive cyberattacks. Its sites were defaced in Belarusian with a warning that no one will escape responsibility, and its main website went offline.
It says no databases were compromised and no legally protected data leaked.


ILYABOEV.COM retweeted

holy f*ck, web designers have NO IDEA what’s coming after them in 2027
the ones learning AI tools right now are getting ahead. the rest might be fighting for jobs they used to take for granted.
7 GitHub repos every designer should know before it’s too late:
1. Graphify
137k stars and in Y Combinator. point it at your old projects, brand PDFs and screenshots, and Claude gets a memory of everything you've ever designed. "what did this client hate last time?" answered in seconds
github.com/Graphify-Labs/gra…
2. Awesome DESIGN.md
84 design systems pulled from real sites, each one a single markdown file. drop it in your project, say "build me a page that looks like this", done
github.com/VoltAgent/awesome…
3. Hallmark
a design skill from Together AI that refuses to look AI-generated. 50 themes, checks every page in a real browser, and /hallmark redesign rebuilds any old page
github.com/Nutlope/hallmark
4. Huashu Design
one sentence in, a launch animation, clickable app prototype, editable PPT or infographic out. it shows you 6 directions first, you pick 3
github.com/alchaincyf/huashu…
5. Designer Skills Pack
273 skills and 76 commands for Claude Code: research, design systems, UI, interaction. a whole design department in one install
github.com/Owl-Listener/desi…
6. Motion Design Skill
LottieFiles taught AI to think like a motion director: timing, easing, choreography, Disney's 12 principles adapted for UI. this is where the "feel" comes from
github.com/LottieFiles/motio…
7. Blender Agent Skills
22 pro Blender workflows for Claude Code: modeling, materials, rigging, animation, rendering. the full 3D pipeline, not just "make a cube"
github.com/EL4CTEO/blender-s…
the cell you're watching?
built solo with Claude Code plus a few of these tools. no agency, no team, no After Effects.
want to make something like this?
like + save this post, comment "CELL" or DM me and I'll send you the exact prompt.


ILYABOEV.COM retweeted

想了解臭名昭著的朝鲜黑客组织 Lazarus,可以看看 Cipher 拍的纪录片《How North Korean Hackers Are Stealing Billions》。
Cipher 专做犯罪和地缘政治题材,看他们的纪录片跟追剧一样。这部片长 1 小时 20 分钟,把这支朝鲜国家队从头到尾讲透了。
Lazarus 可不是普通黑客,它是朝鲜国家养的「犯罪企业」。大多数黑客都是从小被选中的数学天才,每天工作 15 到 20 小时。Lazarus 的 KPI 只有一个:给政权搞钱,大头流向核武。
片子从朝鲜战争、主体思想和饥荒讲起,先讲清楚这个国家为什么会养出这么一支队伍。
然后按时间线一路往下:
① 1980–2000 年代伪造超级美元;
② 2014 年黑索尼影业,起因是那部《刺杀金正恩》;
③ 2016 年孟加拉国央行 SWIFT 劫案卷走 8100 万美元,还让打印机打不出转账记录,好拖延被发现的时间;
④ 2017 年的 WannaCry,用的是泄露出来的 NSA 漏洞「永恒之蓝」,波及约 150 个国家、20 多万台电脑;
⑤ 转战加密:Coincheck、Ronin (Axie)、WazirX,2025 年 Bybit 被盗 15 亿美元,再到现在 2026 年的币安。
------
币圈钱多、盗完还有机会全身而退,Lazarus 只会一直盯着挖漏洞。行业是时候团结起来了,我们面对的是一整个国家机器。
ILYABOEV.COM retweeted

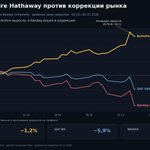
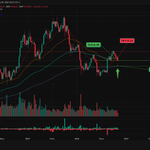
Of the 5 Cyclical bull markets within this secular bull that started in 2009, this one is currently the longest running and best performer.
Does it have legs due to the massive capex and AI backing?


ILYABOEV.COM retweeted
‼️ UPDATE ON THE BINANCE HACK:
Whoever emptied a Binance hot wallet had 50 authorisations signed with that wallet's own private key, on-chain data shows.
Under Ethereum's EIP-7702, an authorisation is a signed permission that lets a wallet hand control of itself to code.
Each one works only for the wallet's next transaction number, its nonce. Binance's wallet was still sending transactions, so that number kept moving.
The sender didn't know which number would be live, so they packed all 50 into one transaction, Blockaid says. One matched.
That one installed a sweeper contract on the wallet. Blockaid found that only the Tornado Cash-funded sender can operate it.
Minutes later it emptied the wallet of $1.6B in USDT, 167,464 ETH and 60+ other tokens.
Only that key, or the system that holds it, can produce those signatures. How the sender got them is unknown.
Across Ethereum, Bitcoin and Tron, at least $5.57B left Binance-linked wallets.
Binance says user funds are "completely safe" but has not explained how.


ILYABOEV.COM retweeted

if you still haven't tried these 7 GitHub repos, i genuinely don't know what you're doing
these open-source projects can turn your computer into an entire Wall Street-style financial research lab
AI trading agents, hedge fund strategies, market analytics, quantitative models and automated trading systems
and the craziest part? most people have no idea these exist
here are 7 repos you need to try:
1 → TradingAgents
an entire AI trading team with analysts, bull and bear researchers, traders and risk managers debating market decisions
github.com/TauricResearch/Tr…
2 → OpenBB
a financial data platform built for analysts, quants and AI agents, bringing market intelligence and research tools into one workflow
github.com/openbq-org/OpenBB
3 → AI Hedge Fund
build a virtual hedge fund where AI agents inspired by legendary investors analyze companies and debate investment decisions
github.com/virattt/ai-hedge-…
4 → Freqtrade
an open-source crypto trading bot with automated strategies, technical indicators, backtesting and trade execution
github.com/freqtrade/freqtra…
5 → Microsoft Qlib
Microsoft's quantitative investment framework for machine learning, market forecasting, portfolio optimization and strategy backtesting
github.com/microsoft/qlib
6 → NautilusTrader
a high-performance trading engine built for event-driven strategies, historical backtesting and automated execution
github.com/nautechsystems/na…
7 → Microsoft RD-Agent
AI agents that automate research, discover quantitative factors, write experiments and optimize machine learning models
github.com/microsoft/RD-Agen…
7 GitHub repos
an entire open-source financial research stack
i won't say anything more...
ILYABOEV.COM retweeted

F*ck Saturday nights.
• Open Google Trends
• Find a problem people are actively searching for
• Turn the solution into an AI eBook
• Price it at $19.99
• Sell 5 copies a day
That's an extra $2,998/month in revenue.
Here's exactly how it works:
ILYABOEV.COM retweeted

Scientists have gave us one of the most detailed looks inside a human cell we have ever had.
Via: Gaël McGill & Evan Ingersoll


Readers added context they thought people might want to know
This is a 3D digital rendering of a eukaryotic cell by Gaël McGill and Evan Ingersoll created 2009-2015 as an educational visualization using molecular data, not a real photograph or direct scientific observation.
gaelmcgill.artstation.com/projects/Pm0JL1
newsweek.com/fact-check-vir…
mymodernmet.com/eukaryotic-cel…
ILYABOEV.COM retweeted

You might just want to stay offline for the next few days, BTW.
These newly discovered PHP vulnerabilities are no joke.
PHP powers about 70% of the global internet, and these are 'critical vulnerabilities'.
Expect massive data breaches, website outages, malware, and remote hacks of 'smart appliances'. Your passwords, personal info, credit card details, and emails are vulnerable.

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.