



Dewcode retweeted
Hey everyone!
I've been getting a lot of DMs for guidance, so decided to take action on it.
I'm excited to help folks out and give back to the community via Topmate. Feel free to reach out if you have any questions or just want to say hi!
I'm at topmate.click/ungi8

Dewcode retweeted

I just published another write-up — how I turned a Self-XSS into a Reflected XSS. Give it a read & any feedback is appreciated. 🙂
#infosec #XSS #bugbounty
medium.com/@mr_yogii/401c264…

Dewcode retweeted
This is my first writeup so please give feedback on this:
How I found Second Order IDOR and earned a reward medium.com/p/how-i-found-sec…
#bugbounty #hackers #infosec
Dewcode retweeted

I have released a Browser Extension to send all your browser traffic ( kinda burp ) to your own hosted server
Link: github.com/0xdln1/TrafficLog…
#BugBounty

Dewcode retweeted
First 4 Digit Bounty & First SQLi In my Life 😁 at @intigriti And Got Accepted 😊 Thank you of all of you guys ❤😊.

Dewcode retweeted

Hello Everyone 👋
I am looking to work with people who want to grow into cybersecurity field, by doing hands on practice on real applications.
🙋 If you're interested or know someone who might be, please share this.
forms.gle/KY2UB95zcojhENGK6
#HiringNow #cybersecurity #Hacking #BugBounty

Dewcode retweeted
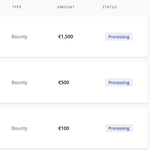
I have got rewarded €500 for An IDOR at @intigriti . Thanks @dewcode91 Bhaiya for the help. #BugBounty

Dewcode retweeted
My 2023 #BugBounty Recap
- Earned 46,369$ in Bounties ( all platforms combined )
- Made it to top 20 in @intigriti
- Top 3 in 2023 Q1 @intigriti
- Able to maintain streak for 12 months in @Hacker0x01 @intigriti and @Bugcrowd
- Crossed 1000 reputation @Hacker0x01


Dewcode retweeted

Ways to leak oauth code in app:
* Bad redir URL host (can redirect to badexample[.]com not just example[.]com)
* Bad redir URL host via . regex issue (can redirect to wwwXexample[.]com instead of www[.]example[.]com)
* Bad redir URL path (redir to a path the attacker can leak via application logic)
* Parameter injection in redir URL %3f -> ? adding parameters or breaking restriction logic
* HTML Injection + permissive redir URL path (img tag + meta tag referrer policy)
* PostMessage leak of URL
* Open redirect
Got any others?


Dewcode retweeted

4 reasons why you are not finding bugs:
• You're switching from targets too much
• You aren't spending a lot of time on bug bounty hunting
• You only run automated scans without understanding what works and what doesn't
• Your target isn't feature-rich or is a static web app
Dewcode retweeted

Never expect anything after reporting a bug. Unmet expectations lead to frustration which might eventually lead to burnout.
#bugbountytips
Dewcode retweeted

I just published a blog post for the people that want to get into bug bounties. I hope it helps people that are thinking about doing bug bounties, but haven't started yet. It explains what to expect and how to deal with common problems / situations: shubs.io/so-you-want-to-get-…
Dewcode retweeted

Have fun while you Hack, most of the magic comes when your relaxed so setup a supportive environment if you can :) take lots of breaks, water, healthy food and sleep, if your in it for the long run to seek out balance :)
Dewcode retweeted

Bug bounty rules:
- Go deep
- Focus on areas that other people don't/can't
- Read the documentation
- Don't compare yourself to others
- Try everything
- Detach from the outcome


Dewcode retweeted
Nuclei reaches 10K 🌟on GitHub 🎉
To celebrate this, we're giving away 1 @Burp_Suite pro license.
To participate, retweet this and comment with the most impactful bug/bounty you have found using nuclei.
github.com/projectdiscovery/…
#hackwithautomation #security #oss #bugbounty


