

@fd_ripatel
🇺🇸Account based in
About this account
- Account based in
- United States
- Connected via
- United States App Store
Account-level information from X, not a live location or the device used for a specific post.
x86 and black metal. retard in motion
Chicago
Joined June 2024
- Tweets204
- Following99
- Followers418
- Likes34K






ripatel ✠ retweeted

"We disabled PIE on nodejs for a 0.3% perf win on an obsolete register-starved architecture that is used by nobody"


nodejs linux official builds are no-pie by default for perf reasons. some distributions like debian/alpine rebuild node, which can enable pie
here's a tracking issue for it: github.com/nodejs/node/issue…


The only way out is hardware sovereignty. War on closed models
xitter.cf/fd_ripatel/status/2110…

I love you @intel.
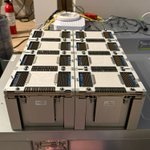
16x Intel Gaudi2 HL-225 bedroom setup. Totaling 1.5TB HBM2e with 38.4TB/s memory bandwidth. Perfect for GLM and Qwen. 38.4Tbps bisection bandwidth on UBB, 2.4Tbps QSFP-DD scaleout.
Total cost less than 2x RTX PRO 6000.

ripatel ✠ retweeted

Pour ceux qui n’ont pas compris :
Dans 5 ans ils vont defoncer les portes d’immeubles et entre chez vous pour vous tuer vous et votre famille


x86 CET-{IBT,SS} coming to Linux {KVM,PL0,PL3}!
Kernel shadow stacks are the final battle. x86 FRED helps by removing hell like IDT nested NMIs.
Fighting with ERETU to 32-bit compat mode now.
arm64-level control flow security on x86 soon.

Wiwynn chassis with MegaRAC SP-X BMC.
Unmodded, the fans run at 20k RPM and consume >1kW power.
But hacked BMC, it's so quiet, I sleep next to it! It shall keep me cozy during Chicago winter.


Linux 7.0 still does not support Intel CET indirect branch tracking (IBT) in usermode.
Intel CPUs supporting IBT first appeared in 2021.
Here's my patch series: lore.kernel.org/lkml/2026051…

This came up while adding control flow integrity to Firedancer's sandbox.
One of the best Linux x86 jails out there, enforcing process isolation, namespaces, strict seccomp, landlock, MPK (user protection keys), CFI, and soon more.
github.com/firedancer-io/fir…

ripatel ✠ retweeted

Today we revived Richie's old blog, bpf.wtf. We'll be pushing a few PRs to add the new syscalls and keep it up to date. To this day, it's still one of the best resources for learning sBPF Assembly. No more Wayback Machine! Compiler disrespecters rejoice!