

Pinned Tweet
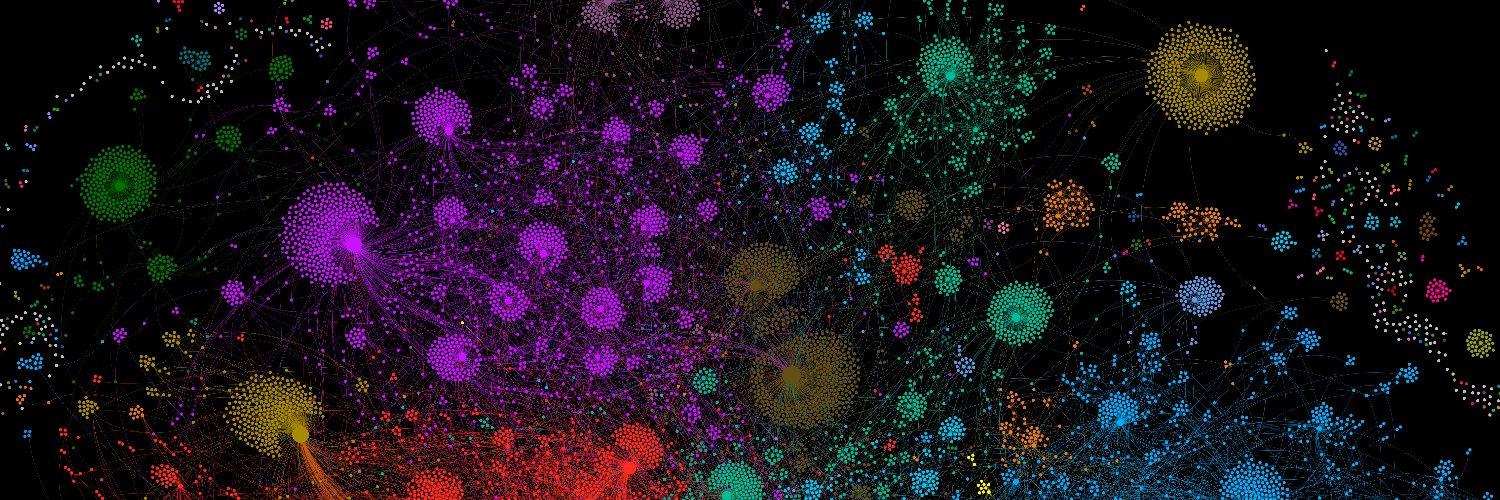
Cómo se siguen entre sí 1.168 cuentas de bancos, ejecutivos, periodistas, medios de comunicación especializados y generalistas, fondos de inversión, economistas, fintech, representantes gubernamentales, entes regulatorios e influyentes varios tanto españoles como foráneos. – at Madrid, Spain

Jose Blanco Oliver retweeted

Maybe important to repost this now that everyone is getting hacked
If you have a VPS, I recommend you to get if off the public internet and into a Tailscale network and Cloudflare Tunnel ASAP
It doesn't matter you have SSH key login, this is about exploits and vulnerabilities AI is finding
There's 2 ways into a VPS:
- via your site/app (like the PHP exploit of this week with a file upload hack)
- via your server (like hacking into SSH or some open port)
The site/app side you put on a Cloudflare Tunnel and then with the default Free Plan it has WAF security enabled by default and they jump on new security exploits fast, it means that the only way to reach your website is via the Cloudflare Tunnel, your server does not respond to port 80 or 443 anymore
The server side you put on a Tailscale network which is like your own private network that nobody can access but your own devices (like your laptop, your phone and your VPS) kinda like a VPN
Then you switch off ANY regular access to your VPS on the firewall, in my case I use Hetzner and you create a new firewall then empty it and that blocks everything (test it)
How do Tailscale and Cloudflare Tunnel get in then? They don't. They go outbound. They make a tunnel to outside which sends and receives
Now you've reduced your attack vector to Tailscale and your Cloudflare Tunnel, much safer, not perfect btw, but nothing is

When I set up a new Hetzner VPS first thing I do install Tailscale and once I'm in via Tailscale lock down the firewall to only accept web traffic on HTTPS 443 for Cloudflare IPs and SSH 22 for Tailscale IP
That way nobody can get in
I know I keep repeating this but it should be basics of setting up a new VPS
So basic IMHO it should be part of any VPS service to default install Tailscale and enable it so it's the only way to get in
Why?
A VPS server is just like your laptop or destop computer but now imagine if it's connected to the entire internet with 8 billion people that can access it and try hack it
You want to only have it accessible to you
And if you want to host a website on your VPS (like I do), you should only let Cloudflare access your VPS so it can stand in front and block any hack attempts
Never expose a VPS to the world wide web which realistically is the world WILD web
Jose Blanco Oliver retweeted

‼️ Tailscale SSH Flaws Could Let Hackers Gain Root Access Across Servers
Details: cybersecuritynews.com/tailsc…
A new security report warns that Tailscale SSH has flaws that could let a hacker move from one compromised device to root access on other servers. Tailscale SSH lets approved devices log in to each other over a private network. The report lists 11 findings in five groups.
They cover Tailscale’s SSH server, its serve and app connector features, the DERP relay client, and headscale, an open-source server that manages Tailscale networks.
The researcher tested Tailscale 1.104.2 and headscale 0.29.5 between October 22 and October 24, 2026. The most serious group involves Tailscale SSH. Its SSH server runs inside tailscaled, a background program with full root privileges on the machine.
#cybersecuritynews

Readers added context they thought people might want to know
The flaws require an already-approved device in the Tailscale network with SSH rules permitting access/forwarding; they enable post-compromise lateral movement and escalation inside the tailnet, not unauthenticated remote access from outside.
tailworm.com
brandefense.io/security-news/…
tailscale.com/security-bulle…
x.com/mmaunder/statu…
Jose Blanco Oliver retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Jose Blanco Oliver retweeted

OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Readers added context they thought people might want to know
OpenAI may claim a role in the coordinated response and patching process. But the initial discovery and exploit development, however, occurred several months earlier by an independent researcher.
x.com/lcfr_hax/statu…
Jose Blanco Oliver retweeted

The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated.
For more⬇️
ncsc.gov.uk/news/critical-se…

Jose Blanco Oliver retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Jose Blanco Oliver retweeted

CISOs, Security Managers, Developers whoever you are reading this, if you use PHP - you need to put a few people on overtime and lock them in a room for the next 72 hours so they can ensure your attack surface is patched.
Theoretical temporary mitigation's might include the below.
php.ini: session.upload_progress.enabled = Off
Then upgrade to the latest version after 2pm UTC

The @php_net security team has given advance notice of two critical remote code execution flaws in PHP core, both rated CVSS 9.2, with the fix due today, 21st October (tracked publicly as CVE-2026-109618 and CVE-2026-109619).
The official write-up is still embargoed, but that no longer buys defenders the time it once did. Details are already circulating, and the gap between disclosure and a working exploit is now measured in hours, not weeks.
Here is what changed. Attackers are AI-enabled. They reconstruct exploits from public trace data, the advisory wording, the commit diff, leaked researcher notes, and they do it faster than most teams can answer a far simpler question: where do we actually run PHP, and which of it is exposed?
That question is the whole game. If you are inventorying your PHP footprint after the CVE drops, you are already behind an adversary who rebuilt the exploit overnight.
Aether AI customers start from the other side of that race. Our AI continuously maps where PHP lives across your external attack surface, so the moment a flaw like this is announced you are not asking "are we affected," you are looking at the exact endpoints to patch first. Ahead of the patch, ahead of the exploit.
The asymmetry used to favour the attacker. We put the same class of AI on your side of the line.
Jose Blanco Oliver retweeted

The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
Jose Blanco Oliver retweeted

¡Hola, Region of Madrid! 🇪🇸 We’re thrilled to announce that we’re coming to Spain, beginning with Madrid. This will be our first region in Spain and second in the European Union. We plan to launch fully autonomous ride-hailing in Madrid in 2027.
Sign up for future updates: waymo.com/waymo-in-spain
¡Hola, Comunidad de Madrid! 🇪🇸 Nos emociona anunciar que llegamos a España, empezando por Madrid. Esta será nuestra primera región en España y la segunda en la Unión Europea. Planeamos lanzar nuestro servicio de ride-hailing totalmente autónomo en la Comunidad en 2027.


Jose Blanco Oliver retweeted

‼️ UPDATE: A researcher says the Broadcom Wi-Fi router bug affects way more countries.
The vulnerable code is also in ZTE's F680 v4, which ISPs from Spain to Vietnam, Egypt and Moldova offer.
Three Movistar Spain routers appear affected. Broadcom still won't assign a CVE.


Uso OpenCode en Local, sin Console, v2.0.30 → no caigo en ese 1,4 %. La brecha fue del servicio gestionado y solo a usuarios con proveedores externos ligados a la Console. Las claves en tu máquina no estaban en ese backend.

We had a security breach last night related to a large scale distillation attack that impacted 1.4% of OpenCode Console users
We have notified them all this morning via email. If you did not get an email you were not impacted, it was a subset of users who had external providers linked
The incident is ongoing so we cannot share more details at this point but we are working with Anthropic, OpenAI, and Google to remediate
Jose Blanco Oliver retweeted
European businesses are rapidly expanding their use of AI agents. More than half of the AI use among our EU enterprise and business customers now involves these tools, and the number of small business users has grown 8x across the region.
Our latest Economic Research report explores Europe’s shift toward agentic AI—and the opportunity to turn broader adoption into deeper use.
openai.com/index/the-eus-nex…

Jose Blanco Oliver retweeted
OpenCode 2.0
anoma.ly/notes/opencode-2-0/

Jose Blanco Oliver retweeted

New on our Engineering blog: Creating in-house source control.
In May, we merged around 2,500 code changes per day. In September, we merged more than 30,000 per day. As a result, we became bottlenecked by developer infrastructure built for human (rather than agent) scale.
Here, we share how we built a new version control system—and fully migrated our monorepo from git—in five months: anthropic.com/engineering/re…

Jose Blanco Oliver retweeted

💤 El sueño de Alsina
💭 "Lamenté que hubiera comentaristas que se exhibieran incapaces de abordar la historia de Maricarmen con una sensibilidad de mínimos"
👉 Una experiencia onírica donde aparece la recientemente fallecida mujer de 87 años desahuciada hace unas semanas
Jose Blanco Oliver retweeted
We’ve lost an icon. Margaret Hamilton, a computer science pioneer best known for her work at MIT leading development of the flight software for the Apollo missions to the moon, has died at 90. Read about her legacy via MIT News: news.mit.edu/2026/margaret-h…

ALT Margaret Hamilton is reclined inside a NASA spacecraft module, surrounded by control panels and switches.
Jose Blanco Oliver retweeted

.@TravelGov: Irkutsk, Rusia: La Embajada de Estados Unidos está al tanto de los informes de prensa procedentes de la región de Irkutsk sobre un presunto caso de peste neumónica que resultó en el fallecimiento de una persona, así como de medidas de cuarentena y el cierre de hospitales en Irkutsk. Seguimos monitoreando la situación de cerca. El gobierno de Estados Unidos tiene una capacidad limitada para asistir a los ciudadanos estadounidenses en Rusia, especialmente fuera de Moscú. La alerta de viaje de Nivel 4 del Departamento de Estado («No viajar») para Rusia sigue vigente e indica que los ciudadanos estadounidenses que se encuentren actualmente en el país deben abandonarlo de inmediato. Se recomienda encarecidamente a los ciudadanos estadounidenses que planeen viajar a Rusia que no lo hagan, debido al riesgo de detención arbitraria y a preocupaciones de seguridad.


