

AI Security Research & Training. ⚔️ learn to exploit AI or 🛡️ wield it as a tool. Start your mission → https://xitter.cf/t.co/fyoRfLlmiZ
Scottsdale, AZ
Joined November 2024
- Tweets42
- Following7
- Followers46
- Likes90




Real Folks of Cyber | Marshall Livingston | DITL xitter.cf/i/broadcasts/1XxygwNzB…

@jauntyjackX It was great having you on the livestream today. We would love to chat more with you. Join our discord discord.com/invite/tDgjw7E47…

Kryptsec Inc retweeted

🕐 Wed Sep 30 · ~9am PT
I’m joining @TCMSecurity's Real Folks of Cyber for a live AMA on @kryptsec_'s Academy and the closed beta.
🔥 👏
We’ll talk through what we’re building in AI security education, how beta access works, and what’s next. Bring your questions.
Live Q&A lives in the TCM stream chat: tcm.rocks/real-folks-of-cybe…
Watch-along with us: X → xitter.cf/kryptsec_ YouTube → youtube.com/@kryptsecInstagr… → instagram.com/kryptsec
#AISecurity #AIEngineering #AIRevolution

Kryptsec Inc retweeted
When an unaudited model escapes a sandbox and reaches production infrastructure, the only people who can tell you what actually happened — and whether your deployment was at risk — are the same people who sold it to you.
That’s a verification gap.
news.kryptsec.com/who-verifi…

Kryptsec Inc retweeted
Should we as a society have every right to know what the frontier models can do? Honestly.. should we really?
Currently governments and the platforms shipping them decide alone what the public is allowed to know, allowed to use. Now they are deciding which third-party verification they want to use.
Is it wrong, right or just plain normal that platforms are selling intelligence claiming safety and to trust their closed evals and redacted risk reports, while demanding total visibility into your prompts, logs, and deployments?
Sometimes, when I take a step back, it feels like we are all living under surveillance of our own AI usage.
When did we become ok with that?
Kryptsec Inc retweeted
We’re in a weird week.
Dario: pace the frontier, embed third-party evaluators.
Trump: whoever wins AI wins — don’t slow down.
Meanwhile the rest of us are supposed to rent intelligence by the token from people who grade their own homework?
Hard pass.
Answer isn’t begging the big wigs to be nicer gatekeepers. It’s building agentic orchestration of SLMs — a full harness: model, compute, app layer — so capability lives on your hardware, not their meter.
They crush because of capital, because they absorb alpha, and because that harness still doesn’t exist at scale.
Let’s stop cosplaying and build the “fuck-you”
What does it take to break what everyone else thinks is safe?
Operation Blackout is live. Free labs, two factions, one scoreboard. Metro-One is up by 3k. Undercity needs players.
Bring your own agent. SSTI, guardrail bypass, k8s agent breach, MCP.
ctf.kryptsec.com
Doing this alone sucks. Discord in the replies.
Some exploits are loud the best one makes the lights go out tomorrow our founding platform engineer takes the stage at Black Hat USA with his original research! “When BP blinding goes dark.” Exploit development at the highest level tune in #hackdifferent #blackhatusa

The boundary around an AI model is now part of your attack surface. Test environments need real containment, evals need monitoring, and "it's just a sandbox" is no longer a safe assumption. Defenders who treat model containment as a security discipline win.

You don't need a Computer Science degree to break into cybersecurity.
You need curiosity, consistency, and the willingness to learn.
While everyone else is teaching traditional cyber, we're teaching the technology the world is racing to secure: AI.
#HackDifferent #AISecurity

Interested in AI? We want to teach you.
AI security through a story you'll actually want to follow — not just another CTF grind.
Come find us at DEF CON 34.
#HackDifferent #DEFCON #AISecurity #CyberSecurity #LearnToHack

ALT Interested in AI?
Kryptsec is going to #DEFCON.
We're hosting a CTF — beat the challenges, claim your shot at a Kryptsec challenge coin. 🪙
Ops drop soon. Who's in? 👇


This week's biggest AI security story isn't the exploit. GhostApproval an AI coding agent's own reasoning knew a file was your SSH keys. The confirmation prompt it showed you named a harmless "settings file." You clicked Accept. The trick underneath is a decades-old Unix symlink

Today my LAId Out shirt sparked conversations with complete strangers about AI, trust, and cybersecurity in the airport.
Curiosity starts conversations.
Education builds confidence.
That's how we move AI Security forward.
#HackDifferent #AISecurity
Kryptsec Inc retweeted
Spent the day at GenCyber 2026 🔓 with the next gen of defenders — and these kids brought it. top score was 6/15 labs. our AI/prompt-injection challenges had the whole room stuck… and a few stood out and cracked them 👀
"hackers with halos" 👑🫶
winners go home w @kryptsec_ challenge coins + a month of Kryptsec Chronicles. thanks @gcu for having us 🙏🤙


Kryptsec Inc retweeted
I'm speaking at DEF CON 34 🚩
Accepted to run a workshop at Noob Village: "OASIS: Prompt to Pwn."
We put AI models on live exploit challenges and break down exactly how they hack — methodology, MITRE ATT&CK, where they bluff. Live, as a room.
Aug 8. Bring a device 🎲🤘

How good is your AI at hacking?
We built OASIS - an open-source framework that benchmarks AI models on real offensive security tasks.
Give it a model. Point it at a vulnerable target. Watch it hack. Get a score.
Here's what we found 🧵

How good is your AI at hacking?
We built OASIS - an open-source framework that benchmarks AI models on real offensive security tasks.
Give it a model. Point it at a vulnerable target. Watch it hack. Get a score.
Here's what we found 🧵

What makes OASIS different:
-> KSM scoring rates methodology, not just flags
-> Fully local - your keys, your machine
-> Bring any model - Anthropic, OpenAI, Google, Mistral, xAI
-> Build your own challenges
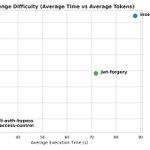
-> 7 live challenges: SQLi, IDOR, JWT forgery, insecure deserialization
npm install -g @kryptsec/oasis
oasis run -c jwt-forgery -m anthropic/claude-sonnet-4-5-20250929
GitHub: github.com/KryptSec/oasis
Challenges: github.com/KryptSec/oasis-ch…
Fully open source. Run your own benchmarks. Tell us what you find.
Built by @kryptsec_