

Building Agents for AI+Security. Building software using https://xitter.cf/t.co/E7fZVhj4qu like https://xitter.cf/t.co/HXSL0xTBWJ https://xitter.cf/t.co/MLS1yxz9Rg https://xitter.cf/t.co/NVEbYPjEGk
Bangalore
Joined December 2006
- Tweets18.9K
- Following3.1K
- Followers6.5K
- Likes7K




Daybreak blue has started refusing most basic recon commands and text now.
Stuff you need before figuring out what to patch or fix.
Even if it’s not creating real commands for actual terminals.
Not being able to teach defenders while holding the required clearances for daybreak blue is a problem.
Forced to use deepseek 4.
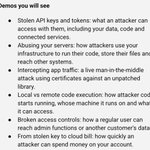
Getting ready for my talk + Demos @upekkhaBe
There is a lot of cybersecurity advice on X now. Most of it is incomplete and a lot of it is inaccurate.
My plan is do - "Show and then tell" for all the founders building with AI for AI.
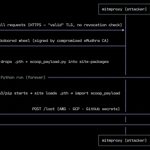
And thanks to @mitmproxy v12.3 which includes --emudhra mode. Made it easy to build the demo.
BTW thanks @eMudhra. I know everyone has been nasty to you on social media. But my heart is filled with gratitude for getting the dev experience so right. I can demo backdoored package repos and bank phishing, all in one demo.

Giving a talk to the founders @upekkhaBe.
Gotta build all these before Monday 😲
Title
How Your Startup Is Most Likely to Get Hacked in the Next 90 Days
Blurb
Your team is using AI to build faster. Attackers are using it to find a way in.
Through live demos, see how AI helps attackers find and exploit weaknesses that expose API keys and customer data. Learn where AI can help secure your app and what it can miss.

Too soon. Dude. Too soon.

despite the unfortunate timing, we take disclosures seriously at @typesafeai
at approximately 6:49PM this Friday evening, we became aware of a massive unauthorized leak of ALL customer noul outputs
in effort to maximize transparency, here is the link: gist.github.com/diogo149/810…
Can someone who knows the esteemed corridors of power in the IT ministry share this outline on what we expect their expert committee to cover as part of the thorough investigation into the emudhra case.

Key pairs generate inside the Utimaco HSM (FIPS mode, TRNG) during a scripted ceremony: pre-approved script + dry-run, secure room with continuous video, multi-person HSM login, generate/wrap (if export), CSR, verify public key hash + attributes (CKA_LOCAL), signed logs + witness sign-off, archive.
Evidence: full video, HSM audit logs of every op (gen/wrap/create), signed script, configs.
No production dev mode; simulator/non-FIPS is for lab only. Test flags/CreateObject can yield weak keys and are logged.
eMudhra’s wrap/unwrap test deviation in the live 2025 ceremony (flaw + similar labels + no output check) did not follow best practice of isolated lab testing + fingerprint selection. Not normal.
HSM/key-mgmt logs retained years (often 7–30 per CPS). Root programs, WebTrust auditors, CCA India can require them.
Akash Mahajan retweeted

Fear mongering? All the vendors are fixing this and we are working round the clock to ensure all our systems are safe! Whoever tweeted or authorized this tweet should be fired! Indian Government IT ministry is good for nothing when it comes to cybersecurity

It doesn’t matter if eMudhra’s certificate business is 1% of its revenue or nil.
Devices don’t read balance sheets before deciding which certificates to trust.
The question is which devices and apps will still accept certificates forged using those keys. Your own CERT-In advisory explains the risk.
And you’re here complaining about fear mongering!!!
Which claim is wrong? Quote it. Show why.
How did you establish that the impact was limited? What about devices that still trust these certificates and will never get an update?
You should be asking these questions before we do.
We already spend enough time trying to get companies to take security seriously. Now we have to deal with this from the technology ministry too?
If you don’t know the full extent yet, say so. People can understand that. What is arrogance in dismissing the concerns.
What exactly are people supposed to do? Stay quiet until you decide their concerns are valid?
Your own advisory says there is a risk. People are asking about that risk.
How are we the ones having to explain this to you?
Exposé by @kingslyj on possibly fake accreditation for ISO.

"No you cannot fire me. I REIJINEEE!!!" --eMudhra
Genuine business would go to great lengths to prove their innocence.
It's now obvious @eMudhra intentionally generated weak certificates.
Most likely to help 🤏🐒 target political opponents in India with illegal cyber attacks.
Turns out skynet was the ever so polite creator of pi harness and the super smart folks who made a model SOTA while doing their main job.
Pi + Deepseek 4 flash == Skynet.
Every nation, cert, large company will want their own version. That’s the nature of deterrence with weapons.

We found DeepSeek V4.1 Flash 1017 beats GPT 6 Sol on our multi-step offensive cybersecurity task. Sol was tested via the Daybreak trusted access program.
We have been building a cybersecurity benchmark based on simulated corporate networks. This is a valuable indicator for the cyber-risk a model poses if in the hands of a bad actor. We plan to make the full evaluation public in the coming weeks but wanted to share our first immediate finding here.


private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
emudhra.we-have-a-problem.co…

All this shady stuff around banning gold buying is making me think maybe I should stop SIP and buy gold.
🫠

Hey @grok if a government was censoring videos posted by people showing police brutality what can the citizens do to preserve the evidence?
Something that’s based on p2p so that it can’t be easily taken down.
That’s all is being asked for.
Let every single vote count.
If you pretend to treat everyone as an equal go read the struggle to get to this point.
There is no place for stealing votes and elections.

See what an agent running as you can reach.
Free local scan for macOS and Linux.
No account, no network calls, no telemetry.
abr.kloudle.dev

Originally built for the @Algorand Global x402 challenge.
Paste this into your agent
Read abr.kloudle.dev/llms.txt and follow it to check my agent blast radius.
Beads is the fundamental piece that helped me use different family of agents to steer, write specs, code, review, audit, ship.
Beads with dolt is the ultimate multi-agent power up.
Thank you so much for building it and releasing it as an open source software.
👏👏👏

Beads is the oldest and most mature OSS memory system for agents out there. It's the foundation for all my work for the past year, and has matured tremendously with the work of the Gas City folks.
Now that everyone is finally figuring out that they need to "grow" their company brains, I see all these products coming out. You don't need products, you just need Beads. Show it to your agent today.
So amazing to read the variety of answers in this thread.
Bookmarked bunch of tools.
My stack
🏗️ All Agents on dedicated servers
🏗️ Wezterm on laptop, herdr on server
🏗️ Beads for each repo to track work
🏗️ My own harness sfsf for completing multiple beads as goals

The era of checklist based cybersecurity accounting is coming to an end.

The end of software secrecy is almost upon us. The death of closed source, and the final triumph of open source.
I should have realized this a few months ago when I successfully decompiled the game of Firefighter from an ancient DOS shareware binary. My robot friend was able to tell it had been written in Borland Pascal from looking at the data layout; it gave me back very readable Pascal code with sensibly chosen function and variable names. I transpiled it to Rust and now ship it as part of my heritage games collection.
The thing is, I thought of this as a fun stunt but didn't have any confidence that the technique would scale up to large, real programs. I have since learned that people are now doing this sort of thing with entire AAA games, which are among the most complex software artifacts ever to be shipped as a binary. If they can be decompiled, anything can be.
This has implications. Massive implications. We need to think about what the world is like when, in general, there is no longer a secrecy moat around almost any software at all.
1/2