
RTs aren’t endorsements. Math, science, maps, nuance. Pragmatic Green & Autodidact.
Joined March 2012
- Tweets20.1K
- Following7.5K
- Followers357
- Likes31.7K


Pinned Tweet
When you dig down into the thought process most of them took, you realize, most of them are just really fucking stupid, and clueless, and afraid and bombarded with nonstop fearporn 24/7. The boomers have big screens and the zoomers have little screens and WE ALL FALL DOWN.
This Post is from a suspended account. Learn more
Theodor von Böngitz Adorno retweeted
Lots of people frame themselves in the press as ‘democratic strategists.’ Replace that term with ‘thieves.’ newrepublic.com/article/2163…


Theodor von Böngitz Adorno retweeted

“a bursting AI bubble would be a much bigger shock to the economy than the bursting IT bubble at the end of the 1990s that brought us to the edge of a liquidity trap. Yet the Fed has much less room to cut rates now than it did then: the current Fed funds rate is only 4 percent. So if huge AI spending is a bubble, and that bubble bursts, I can’t see how the U.S. can avoid plunging into a liquidity trap — a situation in which the Fed simply lacks the tools to get us out of a slump. If this should happen, the economy is likely to remain depressed for years.”
-@paulkrugman
Theodor von Böngitz Adorno retweeted

It absolutely boggles my mind that Democrats would consider passing BAAJA, legislation that makes it easier for energy interests to pollute in this way.
nytimes.com/2026/10/24/clima…

Theodor von Böngitz Adorno retweeted

GMO Internet Group CEO Masatoshi Kumagai says that the internet itself is on the verge of collapse due to missuse of AI, and frames this event as a national crisis.


Theodor von Böngitz Adorno retweeted
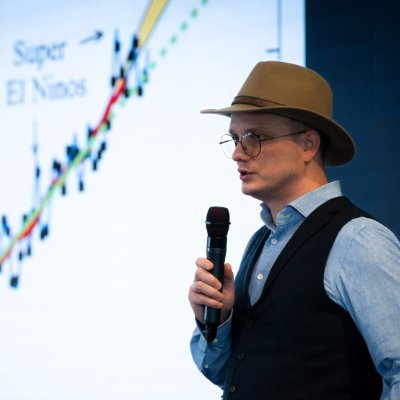
Northern Hemisphere temperature are projected off the chart next week.
The ongoing Super El Niño is starting to increase global temperatures and the weather disasters will come with it.

Theodor von Böngitz Adorno retweeted

APOLLO: AI HAS DELIVERED “ZERO PAYOFF” OUTSIDE BIG TECH
Apollo Chief Economist Torsten Slok warns that massive AI spending has yet to deliver measurable productivity gains across corporate America.
Revenue per worker and profit margins are rising for the Magnificent Seven but remain flat for the S&P 493.
Meanwhile, Gartner estimates $3.5 trillion in AI infrastructure spending could face impairment risk by 2030.
The key takeaway: AI investment is booming, but returns outside Big Tech remain elusive.

Theodor von Böngitz Adorno retweeted

US energy company execs have resigned in disgust as the Trump family is caught secretly expediting the funneling of $25 billion from a sanctioned Russian energy giant in exchange for allowing Russians to obtain a natural gas project in Alaska.
According to investigations by The New York Times and Financial Times, Russia's Novatek allegedly concealed its financial involvement in the American project through a UAE-linked intermediary.
Gentry Beach, a longtime Trump ally and close friend of Donald Trump Jr., signed an agreement with Novatek to pursue natural gas development in Alaska. Reuters documented the arrangement in February.
Meanwhile, Vladimir Putin discussed this cooperation on the Alaska energy project with Trump's representatives, Steve Witkoff and Jared Kushner, during negotiations involving Russia and Ukraine.
The controversy deepened when Polar Train LNG's CEO, Joel Riddle, raised concerns about concealed Russian financing and possible sanctions violations. He departed in September, followed by other senior executives.
The Financial Times also described discussions about a potential arrangement under which Novatek would provide technology for the Alaska project in exchange for sanctions relief benefiting its Arctic LNG 2 development in Siberia.
According to The New York Times, Riddle and two other departing executives warned the Trump administration about the Russian financing and urged officials to investigate.
The White House maintains that the project was mentioned only briefly and that no detailed discussions took place. There is no established evidence that Kushner or Witkoff knew about the allegedly concealed financing. Polar Train LNG denies wrongdoing.
The central question is how a sanctioned Russian energy company became involved in a major American energy venture while Putin was discussing potential economic cooperation with Trump's representatives and a longtime Trump family associate was pursuing a separate agreement with the same Russian company.
Selling Alaska to the Russians or selling Ukraine to the Russians - to the Trump family it's all the same.
ft.com/content/e9cfbfbb-e65a…


Theodor von Böngitz Adorno retweeted
JetBlue is on the verge of bankruptcy, after a bunch of European airlines went under earlier this year. Spirit also liquidated.
The industry is in crisis, only a few big airlines are profitable.
Gotta re-regulate! finance.yahoo.com/economy/ar…

Theodor von Böngitz Adorno retweeted

If you've ever wondered why smart TVs are so cheap, this is why.
@log4j rooted his Samsung and found an always-on hot mic, automatic content recognition, geolocation, network mapping, ad targeting and user profiling, shared with Samsung's "400 partners".
A lot of it can be blocked in <15 min, wrote a basic guide below.
What your TV is doing
The main culprit is ACR (automatic content recognition). Your TV screenshots what's on screen, fingerprints it, and sends it home to build your ad profile. Samsung does it every 500ms, LG every 10ms [1].
What is insane: it happens on connected devices too.
Plug in your laptop, your console, your work machine, and your TV can fingerprint that via HDMI [1].
He also found that if your Samsung doesn't have a mic, it'll look for one from a connected soundbar or bluetooth device.
xitter.cf/log4j/status/211376224…
It's on by default, and you likely agreed to it on the setup screen you clicked through in 10 seconds.
Step 1: Turn off ACR
Samsung: Terms & Privacy → Viewing Information Services
LG: Live Plus
Vizio: Viewing Data
Roku: "Use info from TV inputs"
Sony/Google TV: Samba Interactive TV
Menus vary by model, but those are the names to look for. While you're in there, opt out of interest-based ads, reset your advertising ID, decline every optional privacy agreement, turn off voice recognition, and delete apps you never open.
Step 2: Give smart devices their own network
Put the TV, cameras, speakers and vacuum on your router's guest/IoT network. The logic is simple: these devices rarely get patched. If one gets compromised (getting drastically more frequent with AI), it shouldn't be able to see your other devices or home network.
Step 3: Block trackers for the whole house with DNS-level filtering
NextDNS (cloud-based) is easy and has a solid free plan. Pi-hole is a little bit more work if you prefer self hosting. For simplicity we'll focus on the former.
1. Sign up at nextdns.io (free tier is plenty)
2. Privacy tab: add a blocklist (OISD is a good bet) and turn on Native Tracking Protection for Samsung, LG, Roku, Amazon (see attached image)
3. Setup tab: copy your endpoint
4. Paste it into your router's DNS settings as DNS-over-HTTPS/TLS (or use the IPs + "Link IP" if your router only does plain DNS)
5. Bonus: block outbound port 53 except to your router. Some devices hardcode their own DNS to get around you
Then open the NextDNS logs and watch how often your TV phones home. It's eye-opening. If an app or update breaks, find the domain in the logs and allowlist it.
Why they do this
TV prices are down 97% since 2000 [2]. Most of that is better manufacturing and brutal competition. But once margins on the hardware hit zero, the cost moved to you.
In Q3 2024, Vizio lost $6.7M selling TVs and made $115.8M in gross profit from ads and viewing data [3]. They've said on earnings calls that they keep TV prices low to grow the audience they sell to advertisers. Walmart bought them in 2024.
This isn't a conspiracy theory either. Vizio paid $2.2M to the FTC in 2017 for tracking 11 million TVs without consent. Last December, Texas sued Samsung, LG, Sony, Hisense and TCL over ACR. Samsung and LG have since agreed to stop collecting that data without explicit consent [4].
TL;DR
1. ACR off
2. Ads + voice off
3. Smart devices on their own network
4. NextDNS filtering on the router
Sources:
[1] ACR study: arxiv.org/abs/2409.06203
[2] Cost of US consumer goods: aei.org/economics/chart-of-t…
[3] Vizio Q3 2024: sec.gov/Archives/edgar/data/…
[4] Texas v. Samsung: texasattorneygeneral.gov/new…


Theodor von Böngitz Adorno retweeted

THE PERKINI REPORT: THE 2028 REALITY CRISIS
What if the most obvious financial bubble in all of history turns out to be.... a bubble... and what if that is just really.... bearish?
there were signs, there are always signs 🤣
free link:
hub.tslombard.com/the-perkin…
inspired by @citrini

Theodor von Böngitz Adorno retweeted

Omg.

The GRU hacked into Jared Kushner's iPhone. Dutch military intelligence (MIVD) then recruited a GRU spy who gave them access to the hacked phone. What MIVD discovered was that Kushner had access to two bank accounts --one Azerbaijani, the other Israeli --where Saudi Crown Prince Mohammed bin Salman and Emirati ruler Mohammed bin Zayed deposited money. It sounds like a slightly far-fetched episode of "Slow Horses," but it's real. And it proves just how eye-poppingly corrupt this administration was and continues to be as its "special envoy" decides the fate of tens of millions in Europe in the Middle East. Simply incredible reporting by Matthew Cole, drawn from his new book on Kushner. vanityfair.com/story/jared-k…

Theodor von Böngitz Adorno retweeted

Yikes...worth the 90-second read 😳

Dinner with an exec/friend at a large national property management company tonight. This person oversees ~150k apartments; access to an insane amount of data.
Current multifamily market in most of the country is worse than S&L, .com bust, or the GFC. Worst they’ve seen.
Class A mostly fine, decent rent growth. However:
- credit scores at class A have gone down meaningfully over the past 3 years.
- more people are paying rent via credit card.
- average bank account balance noticeably lower than even 2 years ago
- class A tenants stretched thin, living beyond their means. 20k comes in, 20k goes out every month.
- starting to see these renters move down a tier
Class B:
- simply too many apartments, we built too much new stuff. Ripple effect is enormous.
- fewer renters tomorrow than today. Same store foot traffic noticeably down year over year. Some markets down 40-50%
- considering dropping rents below $700 a month on some 1beds in major southern markets.
Class C:
- looking at degrading NOI. Rents aren’t growing for a long time, but expenses keep creeping up
- more renters are one missed paycheck away from disaster than they can remember seeing in decades
- tenants aren’t paying rent because they simply don’t have it
- wage growth has not kept up
Lenders:
- some major investment funds, household names, haven’t paid their mortgages in 2-3 years. Banks won’t foreclose because “X is a big client.” Mexican standoff.
- a roof leak gets ignored, becomes water damage, then mold, then a down building. Buildings are rapidly deteriorating as some owners choose cash preservation over funding losses.
- number of pre-foreclosure and REO deals is the highest as a % of total units they can recall.
- data providers know it’s bad, but they’re paid to sell optimism to owners/lenders. So every forecast is “it will probably get a little better next year maybe” and that gets regurgitated at investment committees all over.
I asked “how do you think this ends?”
“Not sure. My gut says slowly then suddenly, and things will get really bad. Been doing this 40 years, you can feel it in the air. But, there’s a chance it’s just a decade of tolerable pain. I’m praying for that.”
Theodor von Böngitz Adorno retweeted

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…

Theodor von Böngitz Adorno retweeted

It’s known SARS-CoV-2 evolves to erode antibodies from prior infection/vaccination. We asked: has it also become inherently less recognized by human germline antibodies?
As shown below, answer is yes. ~3-fold fewer naïve human B cells bind newer vs old viral variant RBDs.

Theodor von Böngitz Adorno retweeted

What always interested me about the Elizabeth Holmes story was not Holmes (fraudsters and psychopaths are a dime a dozen in America, not sure why she needs more attention), but what her success revealed about the political and economic elite:
currentaffairs.org/news/2018…


Theodor von Böngitz Adorno retweeted

A visible sign of what AI insiders have been warning about since at least the Mythos release. Acceleration of attack and defense, at inhuman speeds, interacting with the very human systems that need to react to them.

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Theodor von Böngitz Adorno retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.