Threat Intelligence Researcher | Cybercrime News | Staff @vxunderground | PGP - https://xitter.cf/t.co/VWwniNXrEc
Cyberdelia
Joined December 2012
- Tweets2.1K
- Following523
- Followers29.4K
- Likes2.4K





In before a spy chip is found in this thing as well

Your wealth is digital. The device you manage it with should be built for that.
Meet Ledger Atom™: the security of industry leading hardware, the convenience of your everyday apps, plus control over your AI tools, and a rapidly expanding platform of apps, all in one quantum ready device.
Agents propose. You approve. Your Ledger signer enforces.

Anthropic says its research found ‘signs of life for AI worms,’ that could colonize household devices. Experts say they have a point. theverge.com/ai-artificial-i…

Readers added context they thought people might want to know
Anthropic's research used simplified, controlled tests on emulators with trivial unauthenticated access and did not demonstrate a self-replicating AI worm colonizing real devices; caveats and expert skepticism on hype were downplayed.
anthropic.com/research/self-…
reuters.com/business/ai-mo…
newscientist.com/article/259398…
Full picture of the Gamdom exploit
~2.2M stolen on EVM (ETH, BSC, POL, ARB, OP)
965k stolen on Solana
375k taken from TRON and 668k on BTC as well


Approximately 24 hours ago, we detected a potential disk failure on one of our servers. During our investigation, we identified an unauthorized connection on one of our automation servers, which prompted further investigation.
As a precautionary measure, we made the difficult decision to take all of our systems offline in order to fully assess the situation and protect our users.
User funds are safe. We are working to restore services as quickly and securely as possible. We appreciate your patience and will provide further updates as we progress.


Edward Dubrovsky, an executive at a ransom negotiation firm has been identified as the man arrested in Pennsylvania
According to court records, Dubrovsky is now facing conspiracy to threaten to impair the confidentiality of information with the intent to extort money


According to Ledger this stems from a Ledger Device reseller named CryptoBillis located in South East Asia
I'm guessing there was a supply chain breach of some sorts. Consider all devices purchased from CryptoBillis compromised and transfer funds to a new wallet ASAP.
This quoted post is unavailable.


vxdb retweeted

Hello
Unfortunately, @GitHub has banned us. They have orbital nuked the entire malware source code collection.


ZachXBT strikes again, holy shit

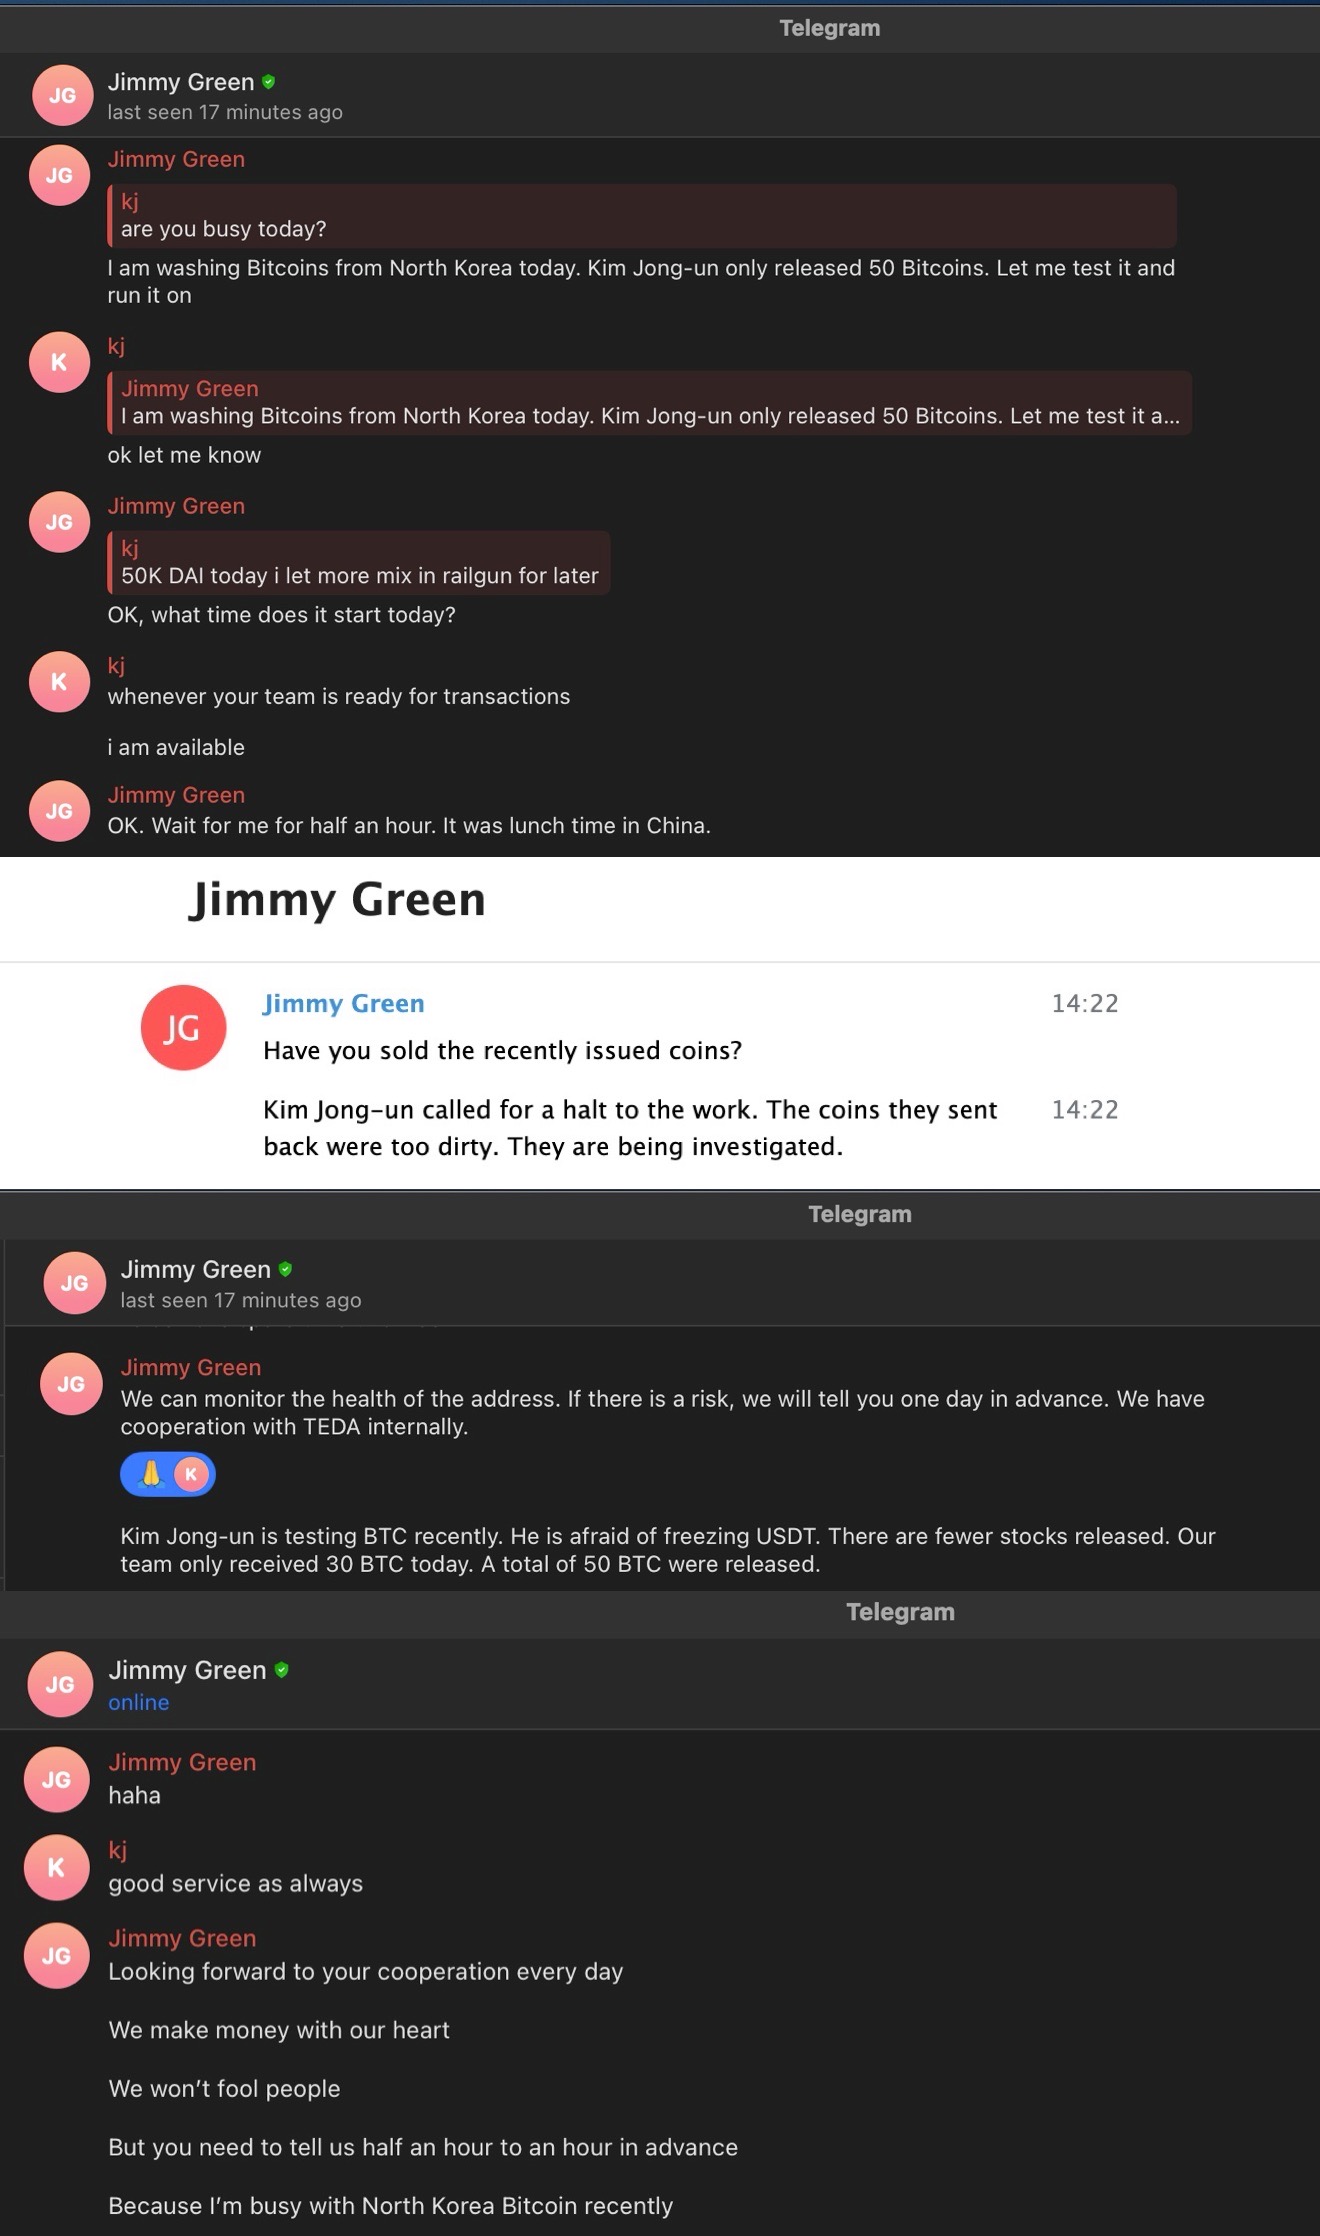
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.