
Just your Average Crypto Miner | Moderator for crypto discord servers | A DYOR-type of person | *stal* following random people on Twitter | opinions are my own
Everywhere and nowhere
Joined June 2020
- Tweets10.9K
- Following5.2K
- Followers1.1K
- Likes12.8K





Helpful Crypto Miner retweeted

🚨 UPDATE: ZachXBT calls out Bitcoin CoinJoin operator Kruw for celebrating 1.6% blockspace usage, alleging Lazarus Group is his largest user laundering stolen funds.


Helpful Crypto Miner retweeted

Okay, here is the anime-lore update for non-schizo-nerds on AI cybersecurity stuff
Basically AI kind of sucked for awhile, but now we've got pretty good with AI stuff. As a comparison, look at AI generated videos from 2 years ago and compare it to now. It's big brain.
Disclaimer: this isn't doomer posting, read fully if you care, or skip and look at the picture of the cat
Some frameworks, such as the infamous ARTEX, utilizes AI which has been trained on like, 40 years of cybersecurity material. Imagine a human being who could think faster, remember more, and troubleshoot faster, and had all cybersecurity knowledge encapsulated into their little mushy brain
Now imagine this person could work in conjunction with other like minded super schizo nerds and communicate with electricity, instead of words, making communication instantaneous with no way miscommunications.
These super schizo nerds don't need coffee breaks, or smoke breaks, or have meetings, or food, or sleep, friends or family. They can work infinitely with zero breaks.
When you take someone who is educated on offensive cybersecurity ("hacking") and give them something like ARTEX, you've essentially made a regular nerd into a super powered super schizo nerd. Likewise, if you give it to a complete noob, even this dorky noob is suddenly exponentially less nooby.
However, just because attackers have ARTEX, and can work faster, stronger, stinkier, doesn't mean defenders are cooked. Attackers can make mistakes, same as AI-powered attackers. But there is one problem I keep seeing now...
Historically defenders have had issues with budgets, fatigue, burn-out, or apathy from the company, customers, or employees. Suddenly defenders have to face supercharged schizo nerds using AI while the organization they are designated in protecting is understaffed, limited budget, doesn't follow properly security protocols (apathy). It makes defense astronomically more difficult.
Defense has always been hard, but when you're defending an organization and you've got 99 dork attackers, and 1 big brain attackers, it can be challenging. Now you've got 75 big brains (supercharged with AI and anime), and 25 dorks, their job is way, way, way more difficult and stressful.
The problem isn't organizations cannot defend with super mega fuck off AI charged attackers, it's that defenders are constantly chained to budget, executives, or employees. This means companies have to do this thing called "caring" about cybersecurity. This means they have to pay people appropriately, actually do updates, force employees (as much as they can) to care, and follow proper security protocols. If companies do not adapt, they're cooked.
This might be easier for large companies, but for small to medium sized businesses and governments (they're not known for their speed...) are in an extraordinarily difficult position. They either have to find the money in the budget, and care, or face the serious possibility to being obliterated by a stinky nerd super charged with AI. Unfortunately, cybersecurity is expensive. For small to medium sized businesses this places them in a really tough spot.
Anyway, that's my goofy layman talk on AI stuff.
pic unrelated (maybe, idk)


Helpful Crypto Miner retweeted

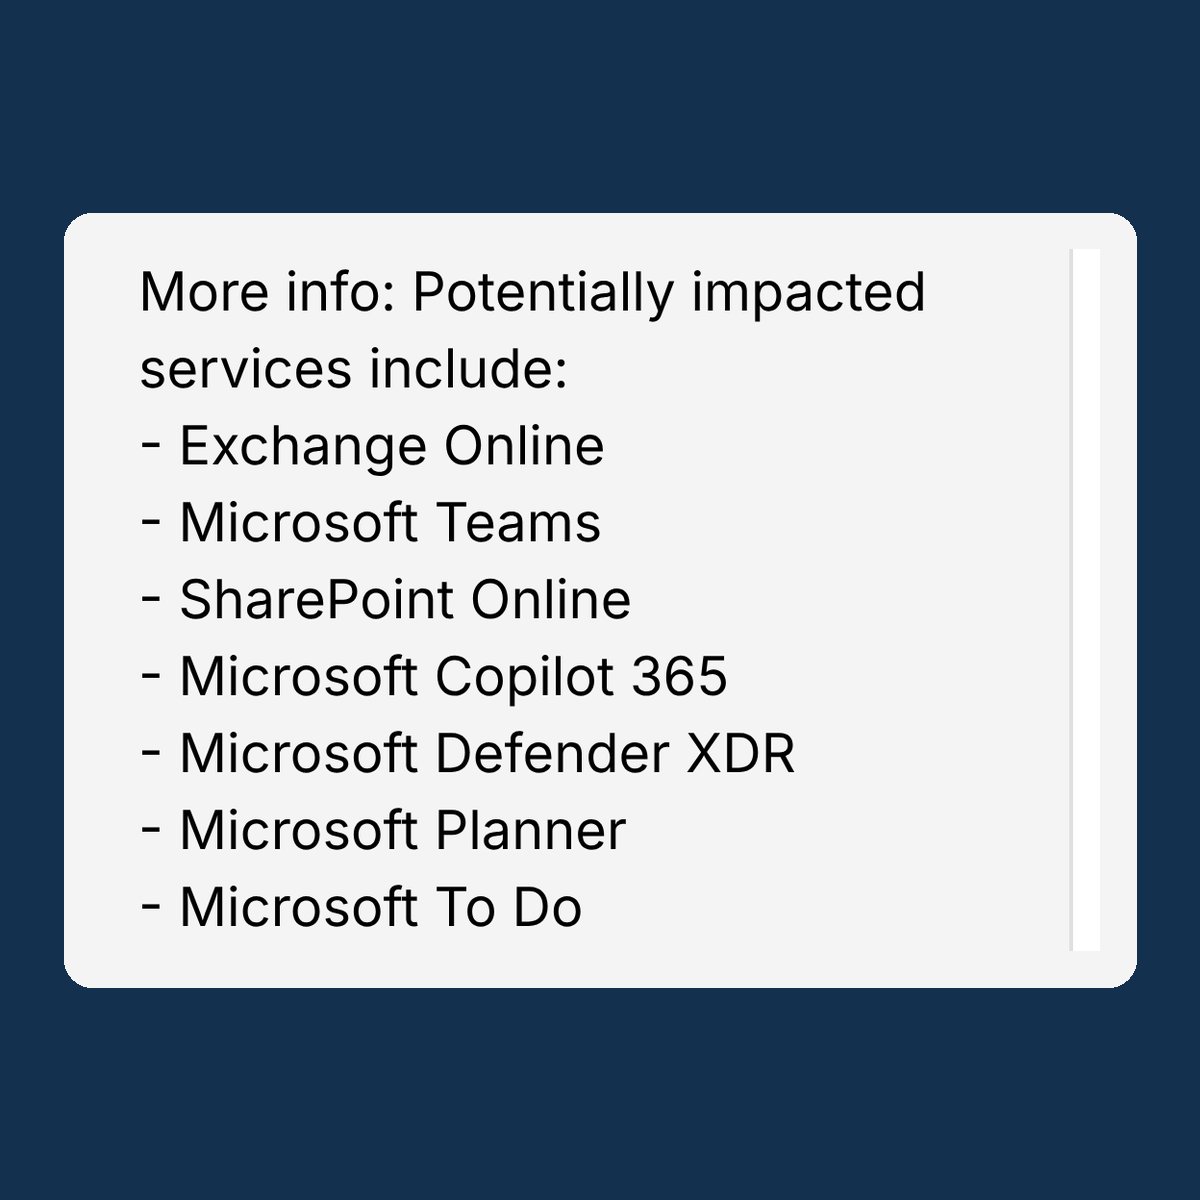
‼️ UPDATE: Microsoft's outage now reaches far beyond Outlook. Teams, SharePoint, Copilot and even its Defender XDR security platform are hit.
Consumers can't reach their OneDrive storage or Office on the web either, TechCrunch reports.
Microsoft first blamed elevated load. Now it says a large number of its servers became unexpectedly unavailable, dumping their load onto the rest. It hasn't said why.
It is restarting the servers with a fix in place, investigating why they show high processor use, and has paused all deployments.



Helpful Crypto Miner retweeted
Unfair that CEOs who aren’t into Asian girls get fewer dating options from spy agencies.
Where are the French/Russian/Iranian honeypots? Not one spy girl sent my way. Are they even trying?
France is excused — their decision-makers aren’t into girls. Everyone else: try harder!

Helpful Crypto Miner retweeted

Pornhub. Tinder. OnlyFans. that anonymous Reddit you think nobody knows about.
a free tool just found ALL of them from one username. 653 sites. 42 seconds.
I ran "elonmusk" through 653 sites and got hits on Venmo. Chess.com. Twitch. Clubhouse. MyAnimeList. Duolingo. even Arduino.
the man is learning Spanish on Duolingo apparently.
no install. no terminal. no API keys. you open one page, press a button, it scans in the cloud and gives you a file with every account found.
csv. json. links. everything.
your digital footprint is way bigger than you think. old forums. gaming sites. dating apps you signed up for in 2017 and forgot about.
I recorded the whole scan. video above.
it's called Blackbird. open source. completely free. 600+ platforms.
run it on yourself before your ex does. or your boss. or HR. or that guy you blocked 3 years ago.
link in the reply
Helpful Crypto Miner retweeted

We know it's not great. For nine years we built and ran our own Layer 1. It hasn't worked.
We're not giving up. Here's the first of many next steps in a new direction:
Zilliqa is becoming the Zilliqa Institutional Layer (ZIL): an Ethereum Layer 2 for regulated institutions.
Usage never reached what a standalone chain needs. Funding and liquidity for standalone L1s dried up. The recent hacks showed how much it takes to secure a chain alone. The data is onchain for everyone to see.
We keep what was great: our partnerships, our community and one token, ZIL.
We cut what isn't working. We stop fighting alone.
We start with a new identity, a new goal and a new path.
What we are building:
- Settlement secured by Ethereum.
- Identity and compliance built into the network, through vLEIs.
- A permissioned market where verified institutions trade with each other. Institutions first, later individuals and agents.
Our partners are even more committed to this future. @ltin_li, the state-backed trust network in Liechtenstein, will operate the sequencer and is becoming a qualified vLEI issuer.
ZIL holders: this move needs no action from you today. We will publish the technical details before anything changes. Any claim, swap or migration is announced on zilliqa.com first. If it's not there, it's not real.
Zilliqa isn't going away. We fight another day.

Helpful Crypto Miner retweeted

FINRA has fined Webull Financial LLC $4.2 million for failing to implement reasonably designed programs for anti-money laundering (AML), identity theft prevention and best execution. FINRA also ordered Webull to certify remediation of the deficiencies in its AML and identity theft prevention programs and retain an independent consultant to address its best execution program.
▶️ Learn more: bit.ly/3Wtm3VJ

Helpful Crypto Miner retweeted
Zilliqa, Previously Backed by Polychain Capital, Announces Pivot from Standalone Layer 1 to Ethereum L2
Zilliqa announced that it will transition from a standalone Layer 1 to an Ethereum Layer 2 called the Zilliqa Institutional Layer (ZIL), targeting regulated institutions. Zilliqa stated that usage on its legacy chain was insufficient to sustain standalone operations; the new network will be secured by Ethereum for settlement, feature built-in identity and compliance mechanisms, and establish permissioned markets for verified institutional participants.
Zilliqa noted that tokenholders currently do not need to take any action, with technical details to be released ahead of the transition. Founded in 2017 by a research team from the National University of Singapore (NUS), Zilliqa raised approximately $22 million across seed and ICO rounds between late 2017 and early 2018, with major backers including Polychain Capital, FBG Capital, and NGC Ventures.

Helpful Crypto Miner retweeted

🚨ALERT: GitBook says an attack using AI agents compromised infrastructure credentials on Nov 2.
GitBook is a platform teams use to create and publish documentation and knowledge bases.
The attacker may have accessed integration tokens, Git Sync secrets, API tokens and questions visitors asked GitBook Assistant.
GitBook revoked all customer API tokens and replaced its infrastructure credentials and secrets.
Users SHOULD now:
- Rotate GitBook and connected third-party tokens and secrets.
-Re-authenticate the GitBook MCP server.
The app, API and published docs are back ONLINE, though some services remain degraded.
Of note, GitBook found no evidence that content was modified.


Helpful Crypto Miner retweeted

💥BINANCE POOL IS SHUTTING DOWN! Bitcoin Miners Must Move Before November 10!
Also have a Braiins 2 Ph/s SHA256 Bitcoin (or BCH) Hashrate Giveaway in the video! You know what to do.
youtu.be/hTLvI0zNJDg?si=JrBN…

Helpful Crypto Miner retweeted
Bro, you can't fucking say openly on social media you just attempted to compromise an organizations infrastructure under your employer and full legal name
Are you actually fucking insane?? Genuinely what the fuck are you thinking???
And how the fuck does this dude know the employees name? Why did the employee openly admit "hehe ye thats me, but no mallace intended, it was my AI agent"
????? WHAT. THATS STILL A CRIME. WHAT ARE YOU TALKING ABOUT.

Helpful Crypto Miner retweeted
INTEL: Over $106 million reportedly stolen from an EU entity's exchange accounts
Helpful Crypto Miner retweeted

WTF!!! The same Android TV box that LinusTechTops covered in 2023 was exposed for running a large botnet
The MECOOL TV box is apart of the XCPE botnet which infected 1.3m devices according to @synthient


Residential proxies, ad fraud, and credential theft have flourished through sophisticated pre-infected device schemes. This research, in partnership with the @motionpictures and in collaboration with @Google, @trendaisecurity , @BlackLotusLabs , and @SecureWithHUMAN, disrupts one of these operators.
Synthient’s Research Team documents its findings in this report, showing how the operators distributed over 1.3 million devices to unsuspecting consumers and how this supply chain pushed numerous backdoors from APSolo to Honeygain.
Read more here: synthient.com/blog/the-inter…

Helpful Crypto Miner retweeted
Elliptic: Binance Hacker Uses CoinJoin for First Time as 44% of Stolen Funds Are Frozen
Elliptic said laundering of the roughly $6.43 billion stolen from Binance has involved 11 blockchains, around 12,000 wallets and more than 40,000 transactions. About $2.85 billion, or 44%, has been frozen or seized, while roughly $3.24 billion remains in linked addresses. Tron was a major route, with funds spread across about 7,700 addresses; the attacker has also begun using CoinJoin, while about $16 million was sent to addresses linked to the earlier Bitget hack.

Helpful Crypto Miner retweeted

THE BLOCK: ZachXBT reported the suspected theft of more than $106 million from multiple centralized exchange accounts held by an unidentified EU entity on Nov. 1.
The onchain investigator said the funds were withdrawn in USDC and USDT, with the attacker subsequently swapping USDC for ETH, converting funds to XMR, and bridging assets across multiple blockchains.


Helpful Crypto Miner retweeted

🚨 We are receiving reports of hot wallets on BTCPay Servers being swept by unauthorized attackers.
If you're running an instance, please shut it down (./btcpay-down.sh) until we complete the investigation.
Helpful Crypto Miner retweeted
❗️ A hacker hijacked Double Counter, a Discord security bot that says it guards 600,000+ communities, and used it to spam about 50 of them with invites to their own server.
The way in on 4 October was an old server that Tellter, the French firm behind the bot, never switched off. It still ran a public Metabase analytics tool.
Tellter treats data tied to ~28M Discord accounts as exposed, including IP addresses and rough locations for ~27M of them and ~1M emails. About 275,000 emails and usernames are already online, Have I Been Pwned says.
When staff reset the bot's token, the attacker read the new one within two minutes. When staff banned the attacker, the bot unbanned them a minute later.

