

QA Engineer that talks about testing, AI and tech news
Joined July 2026
- Tweets570
- Following421
- Followers241
- Likes1.7K




alexusadays retweeted

Foldable iPhone Duo devices are reportedly breaking in large numbers, with displays failing along the hinge crease.
Buyers in Japan, China, Australia, and other countries have reported the same issue. In some cases, the display reportedly fails while the phone is still on display in stores.
The symptoms are identical: after just a few days of use, a black line appears across the screen.


alexusadays retweeted

Pou chèf gang yo ak manm gang yo k ap kenbe kat konpatriyòt nou yo an otaj ann Ayiti:
Mesye nou kidnape yo pa konbatan. Yo se teknisyen nan domèn avyasyon ki fè pati misyon nou ann Ayiti, nan kad yon misyon entènasyonal. Misyon nou an gen sèlman pilòt ak pèsonèl teknik, ki gen kòm travay prensipal fè evakyasyon medikal epi sove lavi moun, pa fè lagè.
Men, nou te kidnape yo yon fason lach pandan yo t ap retounen apre yo te fin achte manje nan yon makèt nan zòn nan.
Se poutèt sa, jodi a nou te lanse yon operasyon militè pou pote yo sekou. Nou gen yon sèl objektif: fè kat konpatriyòt nou yo retounen lakay yo vivan, san okenn mal.
Men, mwen vle pou nou menm, chèf gang yo, konprann yon bagay byen klè: atak jodi a pa anyen devan sa k ap vini si nou pa remèt toule kat otaj yo vivan.
Epi pa pran pawòl nou yo pou menas san fondman. Nou deja fini ak gang yo nan El Salvador, e nou kapab fini ak nou tou.
Nou toujou gen tan pou evite sa.
Remèt nou kat konpatriyòt nou yo vivan, san okenn mal, epi tout bagay ap retounen jan sa te ye anvan kidnaping lan.
Desizyon an nan men nou.
alexusadays retweeted
In response to the eMudhra / emSign certificate security incident we've published guidance for Python users to update CA certificates: discuss.python.org/t/informa…
#security #Python #pki
discuss.python.org/t/informa…

October has been an absolute nightmare for software security.
• Railway: potential exposure of customer secrets
• LiteLLM: compromised release
• OVHcloud CLI: official downloads replaced with malware
• Rank Math PRO: malware distributed through an official download
• ConnectWise: backup application credentials abused to access customer environments
• GhostAction: malicious GitHub workflows targeting developer secrets
• Node.js: security updates announced for supported release lines, with high-severity vulnerabilities
• eMudhra: compromised certificate authority keys, prompting emergency action across browsers and tools, including Tailscale
The systems we trust to build, deploy, secure, and back up our software are becoming entry points.
Your application can pass every functional test while a compromised dependency or stolen CI credential puts the entire environment at risk.
For QA and engineering teams, release integrity, permissions, and secrets handling belong in the definition of quality.
“Works as expected” is only part of the job.
Just used LiteLLM to create my first PHP website. The AI even suggested getting a certificate from eMudhra for HTTPS to protect my login page. The future looks really bright. And the best part, just have some old node js installed already to manage all the packages.
alexusadays retweeted

⚠️ Node.js is vulnerable to remote code execution.
CVE-2026-111497 (high): A Node.js process that decompresses attacker-controlled Brotli data can be made to leak memory or run arbitrary code.
You’re exposed if your app or a library decompresses bad Brotli data (e.g. the built-in fetch(), body-parser)
Aikido detects this. Patches are available.

alexusadays retweeted

Two classes extremely bad cyber vulnerabilities disclosed in the last 24 hours. The first potentially impacts everyone online. The second impacts nearly everyone running a server.
tl;dr: Everyone should upgrade their OS and Browser as soon as possible. If you run a server you should upgrade PHP (or ensure it’s removed if you’re not using it) as soon as possible.
The first class of vulnerabilities is a set of root TLS certificates that were discovered to have a trivial private key. Literally the number 4. These roots were controlled by #eMudhra. The problem is that with that an attacker could create a certificate and, if they could get in the traffic flow, intercept traffic to any site or service. The solution is to stop trusting certificates issued by these vulnerable roots. Upgrading your browser and OS is the fastest way for most Internet users to do this.
The second class of vulnerabilities doesn’t apply to most consumers directly, but does apply to most anyone running a server. These vulnerabilities have been dubbed #php2shell. PHP is one of the most widely used web programming languages. It’s estimated 70% of websites run on PHP. These vulnerabilities allow an attacker to send a crafted set of queries to a server running PHP and potentially take over the server. From there they could potentially read, modify, delete, or repurpose anything on the server. The solution is to upgrade PHP to the latest version ASAP. Even if you’re not using PHP for your web development, it’s often included by default. So make sure it is either upgraded or fully removed.
@Cloudflare received advanced warning of both of these classes of vulnerabilities. We’ve ensured that where we act as a proxy we are no longer trusting the vulnerable roots. We are also reviewing certificate transparency (CT) logs for any sign the vulnerability was exploited before its disclosure. We have not found any evidence but CT logs are not perfect and a sophisticated attacker who knew about the weakness could have exploited it without a new certificate being logged.
For the PHP vulnerabilities, we have deployed mitigations available for all customers for free. Because of the complexity of the vulnerabilities and number of ways it can be exploited, we also released new WAF capabilities that are unique in the industry to catch the exploit based on the response. These too are available for every Cloudflare customer for free.
Even if you are taking advantage of Cloudflare’s protection, it is important to upgrade your OS, browsers, and PHP installations as soon as possible. We can provide a strong bandaid, but the best protection is to fix the underlying problem.
If you’re interested in learning more, you can read our blogs:
Vulnerable roots: blog.cloudflare.com/emudhra-…
PHP vulnerabilities: blog.cloudflare.com/php-vuln…

alexusadays retweeted

🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 nodejs.org/en/blog/vulnerabi…
#NodeJS #Security

alexusadays retweeted

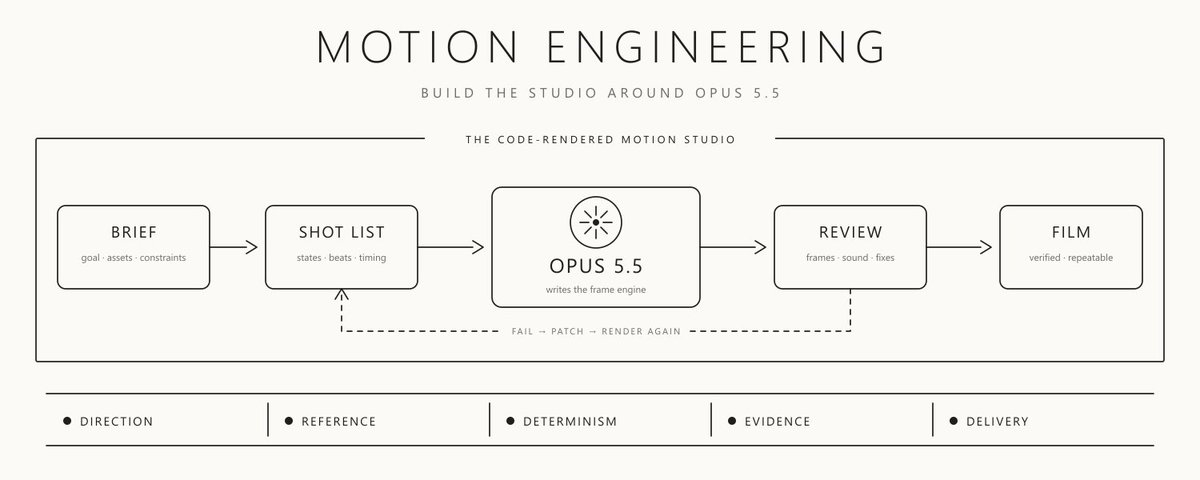
Holy f*ck, Opus 5.5 replaced After Effects
It's f*cking insane…
Drop the PDF below into Opus 5.5 and see what it makes
Then read the full guide on motion design in the article below ↓

alexusadays retweeted

Epic Games released an official plugin that lets Claude Code control Unreal Engine directly.
It connects Claude Code to the Unreal Editor and exposes hundreds of editor tools across 30+ toolsets:
→ Actors, Blueprints and materials
→ Niagara effects, Control Rigs and Sequencer
→ State Trees, widgets and the Gameplay Ability System
→ Automation testing
Install it from Anthropic's official plugin marketplace:
/plugin install unreal-engine-skills-for-claude-code@claude-plugins-official
In Unreal, enable the ModelContextProtocol and AllToolsets plugins, then start the MCP server with the editor open.
Works on Mac, Linux, and Windows through Git Bash or WSL.
github.com/EpicGames/unreal-…

alexusadays retweeted

it's f*cking gold
Unity just opened their game engines to Claude Code
15 github repos that turn Opus 5.5 into a full game studio:
RUN THE WHOLE STUDIO
01. Claude-Code-Game-Studios:
github.com/Donchitos/Claude-…
-> 49 agents from creative director to QA tester, all in one Claude Code session
BUILD IN UNREAL ENGINE
02. UnrealClaude:
github.com/Natfii/UnrealClau…
-> Claude Code docked in the Unreal Editor, 20+ tools for actors, Blueprints and levels
03. Unreal_mcp:
github.com/ChiR24/Unreal_mcp
-> your agent spawns actors, imports assets and launches play sessions in Unreal
04. VibeUE:
github.com/kevinpbuckley/Vib…
-> rides Unreal's own MCP, fixes frame rate drops and sculpts landscapes
05. unreal-engine-skills:
github.com/quodsoler/unreal-…
-> 31 skills for Unreal C++, every API checked against the 5.8 source
06. UnrealGenAISupport:
github.com/prajwalshettydev/…
-> Claude, GPT and Gemini inside your game, even NPCs that run as agents
07. Audio2Face-3D by NVIDIA:
github.com/NVIDIA/Audio2Face…
-> a voice line in, lip-sync and facial animation out, with a UE5 plugin
UNITY AND GODOT
08. Unity-MCP:
github.com/IvanMurzak/Unity-…
-> debugs your project, builds mechanics, and keeps working inside your compiled game
09. ml-agents by Unity:
github.com/Unity-Technologie…
-> train NPCs that learn by playing, with reinforcement learning and self-play
10. godot-mcp:
github.com/Coding-Solo/godot…
-> builds scenes, runs your game in debug mode and reads the errors back
ART AND SOUND
11. CHORD by Ubisoft:
github.com/ubisoft/ubisoft-l…
-> one texture image in, base color, normal, height, roughness and metalness maps out
12. ACE-Step 1.5:
github.com/ace-step/ACE-Step…
-> a soundtrack for your game, under 10 seconds a song on an RTX 3090
13. HunyuanVideo-Foley by Tencent:
github.com/Tencent-Hunyuan/H…
-> drop in a gameplay clip, get sound effects synced to what's on screen
WORLDS THAT GENERATE AS YOU PLAY
14. Hunyuan-GameCraft by Tencent:
github.com/Tencent-Hunyuan/H…
-> one image plus WASD in, playable game video out, trained on 100+ AAA games
15. Matrix-Game by Skywork:
github.com/SkyworkAI/Matrix-…
-> a real-time world you can walk through, and it remembers where you've been
every department of a game studio, one link each.
should i write the full guide to building an Unreal game with Claude?

is it legal?
NVIDIA and Microsoft just open-sourced the pieces of a full 3D studio for Opus 5.5
15 github repos, sorted by what you want to make:
GENERATE 3D ASSETS
01. TRELLIS.2 by Microsoft:
github.com/microsoft/TRELLIS…
-> one image in, a fully textured 3D asset out, about 3 seconds on an H100
02. Hunyuan3D-2.1 by Tencent:
github.com/Tencent-Hunyuan/H…
-> production-ready 3D assets with PBR textures
03. stable-fast-3d by Stability AI:
github.com/Stability-AI/stab…
-> one photo to a clean UV-unwrapped mesh, built for speed
04. meshy-mcp-server by Meshy:
github.com/meshy-dev/meshy-m…
-> text or image to 3D, then remesh, retexture, rig and animate from your agent
BUILD SCENES AND WORLDS
05. mcp-for-blender:
github.com/ahujasid/mcp-for-…
-> prompt-driven modeling, scene building and edits in a live Blender
06. HY-World-2.0 by Tencent:
github.com/Tencent-Hunyuan/H…
-> text or a single image to a navigable 3D world
07. supersplat by PlayCanvas:
github.com/playcanvas/supers…
-> inspect, edit, optimize and publish 3D Gaussian splats in the browser
08. kit-usd-agents by NVIDIA:
github.com/NVIDIA-Omniverse/…
-> edit Omniverse USD scenes in plain English, plus MCP servers for Kit and Isaac Sim
MAKE A GAME
09. unity-mcp:
github.com/CoplayDev/unity-m…
-> run the Unity Editor in plain English: scenes, C# scripts, assets, tests, builds
10. godot-ai:
github.com/hi-godot/godot-ai
-> 46 tools for a live Godot editor: scenes, scripts, signals, UI, particles
11. unreal-engine-mcp:
github.com/flopperam/unreal-…
-> drive a live Unreal Editor: actors, world building, Blueprints
3D ON THE WEB
12. editor-mcp-server by PlayCanvas:
github.com/playcanvas/editor…
-> your agent builds PlayCanvas scenes and checks they actually run
13. three.js:
github.com/mrdoob/three.js
-> the JavaScript 3D library itself, 115k stars on GitHub
14. react-three-fiber:
github.com/pmndrs/react-thre…
-> build three.js scenes as reusable React components
15. threejs-skills:
github.com/CloudAI-X/threejs…
-> 10 three.js skills for Claude Code, from shaders to post-processing
a full 3D pipeline, and every piece of it lives on github

alexusadays retweeted

We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier. We referred the matter to the FBI, and we’re grateful to the agents and prosecutors who moved quickly to make an arrest. The FBI’s investigation is ongoing and we will continue to support their work.
At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.
We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.
alexusadays retweeted

BREAKING: Ukrainian strikes on Russian technology giant Yandex's data centres have been followed by a dramatic decline in automated online activity, particularly on Reddit, per Euronews
alexusadays retweeted

THE FULL ADOBE SUITE HAS BEEN REWRITTEN IN RUST AND FULLY OPEN SOURCED 🚨
Brandon Thomas, the founder/CEO of ArtCraft has decompiled and rewritten almost every Adobe app and has now released them for FREE.
How long until AI companies shut down the ability to do this?

Readers added context they thought people might want to know
ArtCraft's own GitHub repos and site describe the apps as clean-room reimplementations of Adobe products built from scratch in pure Rust, with no decompiled code. github.com/storytold/phot… getartcraft.com/apps github.com/storytold/vect…
alexusadays retweeted
We announced an agreement to acquire a nationwide low-band spectrum license portfolio that will pave the way for @Starlink to become a major mobile carrier in the US.
With this new spectrum and our Gen2 constellation, Starlink Mobile can ensure Americans have access to high-speed mobile broadband no matter where they are → spacex.com/updates#starlink-…


alexusadays retweeted
BREAKING:
5 hospitals have been closed for quarantines in Siberia due to a possible plague outbreak.
The 28-year-old lab technician Darya Shipilova, died yesterday after breaking a test tube with live Yersinia pestis the Irkutsk Anti-Plague Institute on September 25th while handling samples.
A mask mandate has now been introduced at the huge aluminum plant in Irkutsk.
Some U.S. politicians are now calling for commercial air travel to and from Russia to be stopped until the situation is clarified.
This first symptoms of pneumonic plague typically start about 4 to 7 days after exposure. 200 people are under observation.
