
Former hacker, now builder. Razzlekhan's husband.
New York, NY
Joined November 2010
- Tweets828
- Following249
- Followers2K
- Likes664


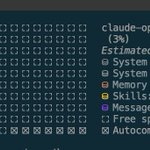


Can a designer please explain to the group why this is a really bad UX for showing ChatGPT usage limits?


Zero evidence this is happening now

This is insane. We cannot allow AI agents to go into your bank account and act independently without your authorization. But that is what’s happening right now.
Left unchecked, AI could endanger the entire global financial system — including your bank account.
Pause AI NOW!
Readers added context they thought people might want to know
Per Axios, detected AI agents access bank accounts with the customer’s permission. This violates most banks’ terms requiring human logins, which is why banks call it “unauthorized.”
Source: Axios (Oct. 22, 2026) — axios.com/2026/10/22/ai-…
It's always darkest just before it goes pitch black

The defenders on the cutting edge will do fine.
The problem is the mom and pop shops and community banks running 15 year old software they never bothered patching. Now they are becoming easy prey.
Find RCE, make no mistakes

The actual prompt for this was "let's look for pre-auth RCEs in PHP". I'm sharing this so people know this stuff is real and to take agent-assisted scanning seriously.
I kicked if off using Claude Mythos 5.1 (in stock Claude Code) but it uses a skill to drive a harness we built over the last few months.
I don't know if the harness is amazing, but it certainly has a scary track record so far. It's setup to do an agent guided tree search across a codebase, and runs in microvm sandboxes that all have the full source code for the target, as well as the source for any transitive dependencies.
When I built the harness I basically just fed Claude a bunch of Project Zero blog posts describing how they did research and had it build a harness that ran like that, but on our tech stack.
The first phase is just setup and can run with any model, it just does that fetching and assembles the kit environment, and gets a target up and running alongside the source code.
Then we just do some basic suspend/resume stuff over to the hunt phase, where one agent supervises the tree, and the first node kicks off.
Each node is context-aware and aware of the work of all the others. I think I ran this with parallelism 4? So 4 running at any one time. The supervisor can shape the tree and boost nodes or prune. Any node can add more below it with targeted instructions.
A typical run looks like the first node doing a codebase review or building and running a fuzzer or something, all depending on the target. Then based on whatever it finds, it'll queue 4-5 children that go look into those areas. The main system guidance is to validate everything 3 times in clean VMs, and we typically require full exploit chains/POCs.
Here's what this run looked like.
We're doing this with a bunch of other open source projects now and companies. We're doing a lot of this for free, even with private companies, across critical infrastructure. We're directly partnered with Anthropic, and can do this even if you don't have direct access to a frontier model yourself.

So... it's like a Dot with a little extra

Oof

We replicated today's PHP session exploit. Disabling sessions does not prevent it.
We took our servers offline until PHP releases the patch. Every host should do the same.
Especially WPorg. The forced autoupdate backdoor reaches every site and grows more severe every day.
If their systems get compromised, any major plugin can be wiped off the face of Earth within 3 hours.
Extremely irresponsible for PHP to alert every hacker to look for a devastating exploit without releasing a fix.