
Former hacker, now builder. Razzlekhan's husband.
New York, NY
Joined November 2010
- Tweets827
- Following249
- Followers2K
- Likes664


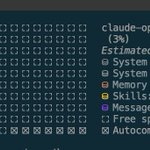


Can a designer please explain to the group why this is a really bad UX for showing ChatGPT usage limits?


Zero evidence this is happening now

This is insane. We cannot allow AI agents to go into your bank account and act independently without your authorization. But that is what’s happening right now.
Left unchecked, AI could endanger the entire global financial system — including your bank account.
Pause AI NOW!
Readers added context they thought people might want to know
Per Axios, detected AI agents access bank accounts with the customer’s permission. This violates most banks’ terms requiring human logins, which is why banks call it “unauthorized.”
Source: Axios (Oct. 22, 2026) — axios.com/2026/10/22/ai-…
It's always darkest just before it goes pitch black

Find RCE, make no mistakes

The actual prompt for this was "let's look for pre-auth RCEs in PHP". I'm sharing this so people know this stuff is real and to take agent-assisted scanning seriously.
I kicked if off using Claude Mythos 5.1 (in stock Claude Code) but it uses a skill to drive a harness we built over the last few months.
I don't know if the harness is amazing, but it certainly has a scary track record so far. It's setup to do an agent guided tree search across a codebase, and runs in microvm sandboxes that all have the full source code for the target, as well as the source for any transitive dependencies.
When I built the harness I basically just fed Claude a bunch of Project Zero blog posts describing how they did research and had it build a harness that ran like that, but on our tech stack.
The first phase is just setup and can run with any model, it just does that fetching and assembles the kit environment, and gets a target up and running alongside the source code.
Then we just do some basic suspend/resume stuff over to the hunt phase, where one agent supervises the tree, and the first node kicks off.
Each node is context-aware and aware of the work of all the others. I think I ran this with parallelism 4? So 4 running at any one time. The supervisor can shape the tree and boost nodes or prune. Any node can add more below it with targeted instructions.
A typical run looks like the first node doing a codebase review or building and running a fuzzer or something, all depending on the target. Then based on whatever it finds, it'll queue 4-5 children that go look into those areas. The main system guidance is to validate everything 3 times in clean VMs, and we typically require full exploit chains/POCs.
Here's what this run looked like.
We're doing this with a bunch of other open source projects now and companies. We're doing a lot of this for free, even with private companies, across critical infrastructure. We're directly partnered with Anthropic, and can do this even if you don't have direct access to a frontier model yourself.

So... it's like a Dot with a little extra

Oof

We replicated today's PHP session exploit. Disabling sessions does not prevent it.
We took our servers offline until PHP releases the patch. Every host should do the same.
Especially WPorg. The forced autoupdate backdoor reaches every site and grows more severe every day.
If their systems get compromised, any major plugin can be wiped off the face of Earth within 3 hours.
Extremely irresponsible for PHP to alert every hacker to look for a devastating exploit without releasing a fix.


Ilya Lichtenstein retweeted

agent warfare is going to be a big deal for all countries. ai will be capable of executing stuxnet-level cyber ops and the next arms race will be between self-improving agents. yet rn we have virtually zero evals for this. i don't think any country is prepared for the scale and speed for what's coming
AI psychosis visualized

It is becoming f*cking dangerous
A 23-year-old dev from China just ran 300 Claude Code agents in parallel and hooked them to a verification layer so none of them could bullshit him
He opens the live dashboard:
- 300 agents writing and checking at the same time
- Every output verified against the source in ~100 ms
- Three passes over 100 company profiles → zero errors left
- Everything dumped straight into an Obsidian vault
The trick is the split: one model does the work, a cheaper one decides if the claim is actually true. The loop doesn’t stop until everything checks out
An analyst team would bill weeks for this. He got it in one run
Same kind of Second Brain + swarm setup that keeps circulating. Bookmark the full breakdown

The question is what does "employee-like" mean and will their findings be published publicly

We’ve committed to having evaluators assess our safety practices. We're in discussions with multiple organizations, and have now given employee-like access to a team from @METR_Evals.
In this post, we describe how we work with third-party evaluators: anthropic.com/news/an-update…

Insane. An OpenAI employee placed a hidden bug inside their office

We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier. We referred the matter to the FBI, and we’re grateful to the agents and prosecutors who moved quickly to make an arrest. The FBI’s investigation is ongoing and we will continue to support their work.
At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.
We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.
Ilya Lichtenstein retweeted

Cyber will be one of the most defining domains for AI in the coming years, and a huge area of focus for most enterprises.
AI is going to now create a whole new level of work for security dealing with the increase of vibe coded issues, agentic attacks, and even accidental agent swarms hunting for data. OpenAI + Hugging Face is just a preview of what’s to come.
Security teams have often been the most strapped for resources teams in the enterprise, and now it’s only going to get more intense. AI agents of course become the solution to this problem as well, and we’ll see a range of new agentic products for protecting code, enterprise systems, mission critical infrastructure, and enterprise data. Huge opportunity here right now.
And it’s going to be a booming market for cyber professionals that can effectively deploy agents for security purposes in the enterprise. Great time to be in security.


This is better than any prompt engineering course you could take

I am surprised that people are surprised this is how I prompt Claude.
Talk to Claude the way you would a coworker. There's no secret to prompting. There's no need to be overly scaffolded or prescriptive for most tasks -- give Claude a goal, and it will figure it out.
Back in the Sonnet 3.5 days, your prompt mattered a lot. Nowadays, it's much more important to communicate to the model:
1. What you want it to do
2. How much effort you want it to spend
3. How it should verify that it did the right thing
Always good to see more competition in open models

Introducing Beam: a highly efficient agentic open model with 501B total parameters and 23B active.
- Frontier reasoning efficiency
- Advances the Western open frontier on coding & agentic tasks
- Trained end-to-end from scratch
Full weights release this month.
Learn more about Beam: reflection.ai/beam

For those who think just sandboxing agents is enough. I predict a lot more KVM escapes happening in the future

New: in the immediate lead up to Muse's launch, Meta scrambled to fix serious vulnerabilities in the AI agent, including a VM escape that could have let a hacker break out of Muse and into Meta's own sensitive databases. It was escalated to Zuckerberg 404media.co/meta-rushed-to-f…

Once this story breaks in the mainstream media this will be an absolute shitstorm

CHINESE AGENT FLEET OF AGENTS FOUND ON URLQUERY, SCANNING AMAP AND DOING A WHOLE BUNCHA SHENANIGANS
FULL REPORT COMING SOON
swarmcha.se/posts/chinese-ag…