




Everything is fraud or CVE on the internet. Fatigue.

@_@ retweeted

You've just sold the entire reason for having guns.
"I want to do violence to you, but I can't, because you're armed."
The violent thugs of the world are kept at bay by the possibility people can resist them.

@_@ retweeted
Go forth and open-source every IoT device in your house. Dump their comms. See what they're sending home.
God speed.
@_@ retweeted

the patch basically is the advisory at this point. once cloudflare is seeing attacks in the wild, holding the fix just means attackers know and defenders don't. was there any word on why they waited?

In which a Cuban anchor baby goes to India to promote more infinity Indians in America, calling Americans "stupid" and "dumb" in front of India in the process, absolutely eliminating any hopes he had of running for president.

In Mumbai, Indian External Affairs Minister @DrSJaishankar and I discussed energy security and defense cooperation while reaffirming the importance of advancing the U.S.-India strategic partnership.


I sent the same advice to clients 4 hours ago.

I pre-emptively disconnected ALL my sites / VPS servers from the web
I'll wait for the patch to hit at 2 PM UTC
If you have a PHP website, probably good to take them down until you patch PHP
69.3% of the web runs on PHP so this is going to be intense!
Good time maybe to buy cybersecurity stocks? (not financial advice)

@_@ retweeted

How on earth did this happen:
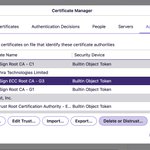
The Indian certificate authority (CA) eMudhra had one job (well, two):
1. Create secure, 384-bit private keys
2. Store these securely and do not leak them
Well, eMudhra chose private keys between 1 and 256 (the numbers!!) and called it a day. WTF


Yes. Today we did. All we had to do was put an incompetent 3-person Indian company in the shared trust pool to pollute and destroy everything.
Complete destruction. ☑️ Good job, internet.

@_@ retweeted

India’s lead “IT specialist” who had “over 15 years of experience” basically secured the network on half the devices in the world with the password equivalent of “123”.
This is the “elite human capital” that our IT industry can’t survive without.

@_@ retweeted

Gross incompetency from Indian certificate authority eMudhra.
You had one job: generate a 384 bit private keys and instead you used: 4, 56, 66, 115, 155, 156, 230, and 237.
This allows attackers to issue certificates for any websites.
Embarrassing that it’s a family business run by largely computer illiterate people. Only 1 of the 3 have a remotely computer-related background and even they never actually worked a technical job in their life. If you look at the LinkedIn, their tech team is young, from tier 3 education and paid sort of bottom barrel.
Imagine how many attacks you can design with AI given the existence of this genre of gross negligence.


Routers, IoT, and embedded are going to get wrecked.
Many people install their Wifi router and never update it again for life.


@_@ retweeted

The situation where a certificate's private key only has 8 bits of randomness instead of 384 is unacceptable.
We should urge all certificate authorities to immediately publish their private keys so that the community can make sure they are random enough.


