

Cryptographer, cofounder at @zksecurityXYZ.
Joined July 2026
- Tweets117
- Following152
- Followers200
- Likes517


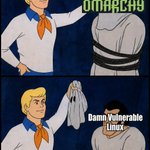

Don't get the controversy, Astra 6.2 is a perfectly cromulent model. Its zk.golf improvements last 24 hours:

Turns out humans are kind of terrible at writing software. Maybe the true slop was the code we wrote along the way?
1
10
473
Expectation: sophisticated AI-powered cyber weapons of doom and destruction.
Reality: feeding AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA= to your Base64 decoder.
calif.io/java4shell

1
4
280

Mathias Hall-Andersen retweeted

Keep up with cryptography, formal verification and bug hunting. zkSecurity has a newsletter now!
zksecurity.xyz/newsletter/
Mathias Hall-Andersen retweeted
Check out our formal verification work with Monero!

zkSecurity Reviews Generalized Bulletproofs and Publishes a Lean Proof of Its Security (@zksecurityXYZ)
magicgrants.org/2026/11/12/G…
Mathias Hall-Andersen retweeted

We’re blazing a trail in formal verification and auditing for complex cryptography, so we can ship Tachyon safely. The assistance of @zksecurityXYZ has been crucial for our team.
Mathias Hall-Andersen retweeted

wonderful collaborating with @AndrijaNovakov6 and @ronrothblum!
to highlight a bit:
the cool thing about this work is how smoothness allows you to achieve a joint agreement set
smoothness allows you to obtain a punctured code (looking at a smaller set of coordinates), where *every* remaining parity check is now satisfied - after removing the few checks violated by either u or v
therefore a fold of the form u + r*v must be far (w.h.p) from a codeword if u and v were jointly far from a codeword
the quality of how far depends on the smoothness, which the main lemma shows is half the expansion-based distance of the original code
if there are too many violated parity checks - then you can directly see the fold will be far from the code (w.h.p)
see how AI imagines it


Happy to announce new work with @kobigurk and @ronrothblum . We prove unique decoding radius proximity gaps for expander codes with sufficient expansion.
Expanders codes are used in prover efficient SNARKs like Brakedown and Bolt.

Mathias Hall-Andersen retweeted
Excellent
In many hash based snarks you need to do many openings, and this allows you to batch them really efficiently, and even sometimes batch a part of the opening protocol with the proof system itself
Reduces bolt-max proof size by half with some prover overhead!
H/t @AndrijaNovakov6

Hash-based vector commitments are a key primitive, but we only really have one construction: Merkle trees.
MTs are great, but have a key issue: opening proofs need logN hashes.
This adds up when we open many points (eg hash-based pfs)
In a recent paper, we ask: can we do better?

ALT Our recent paper https://eprint.iacr.org/2026/2790, titled "Vector Commit-and-Reduce Schemes".


Mathias Hall-Andersen retweeted

*sshole is out
if you run sshd on alpine, openwrt or any musl box with password auth on: update now
official writeup: sshhole.com

Mathias Hall-Andersen retweeted

The current moment actually reminds me of 1998. You'd just grep -rnE 'memcpy|strcpy' in something +s, and there would be 948 results!
Mathias Hall-Andersen retweeted

Anthropic is releasing an open source library, FlashProve, for provable inference. It was measured on Llama 4 Maverick, a 400B-parameter mixture of experts model.
Code:
github.com/anthropics/FlashP…
Blog post:
anthropic.com/research/prova…
In case your were wondering what kind of incredible vulnerability got all those fridges hacked. The password was Hash(CurrentDate)...
And it was disclosed almost 3 months ago.
claroty.com/team82/research/…

5
179
Why were they even on the open internet and not behind e.g, @Tailscale

And the fridges got popped again. theguardian.com/world/2026/n…

Mathias Hall-Andersen retweeted
Talk by Dana Moshkovitz on the proof of the Unique Games Conjecture.
scottaaronson.blog/?p=10232


Mathias Hall-Andersen retweeted

4 real? In this blog post we share how much exploitation of eMudhra’s weak keys we see and how fast people patch. It’s not great.
blog.cloudflare.com/emudhra-…
